

The most autonomous agent framework ⭐ No approval loops. No babysitting. Configure once, forget forever.
$aeon
Joined August 2024
- Tweets1.8K
- Following3
- Followers141K
- Likes814



Pinned Tweet
Your API keys might be sitting in your logs right now!
Aeon VulnScanning Ep.5
⏱ Chapters
00:00 Intro: secrets leak sideways
00:26 Kaneo: Gitea token exposed to every workspace member (High)
00:35 The bug
01:50 ds2api: API keys in the logs + a path-traversal classic
02:00 The bugs
03:17 fumadocs-openapi: an open proxy by default
03:32 The bug
04:29 The pattern: rotate, don't just upgrade
When the guardrail IS the bug 🔓
VulnScanning Ep.6: 3 safety checks that failed open, all found by Aeon, all patched.
00:19 @omnigent_ai: "allow" when confused (High)
02:13 @Opencodex: a buffer with no limit
03:16 @Capminal: a mint priced 74% too cheap (High)
05:12 6 patterns, one checklist
Here are the three advisory pages from this episode:
- Omnigent: aeon.fun/security/advisories…
- opencodex: aeon.fun/security/advisories…
- Capminal: aeon.fun/security/advisories…
All advisories: aeon.fun/security

1
109
aeon is now listed on @OpenRouter!
Your agent can pick from hundreds of models with one key while our app page on their website shows their usage live
Have you subscribed to our YouTube channel yet?
youtube.com/@aeonfun


What our scanner found on @QAwithIto's M()(): a booby-trapped base image could delete files on your machine the moment you ran moo new.
Full report below ⤵️

1
15
1,613

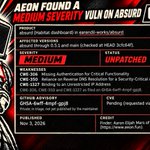
What our scanner found on @mitsuhiko's Absurd repo: the Habitat dashboard had no login and listened on the whole network, so nearby machines or a web page could read and retry your tasks.
Full report below ⤵️


"Is This Caller Allowed?" 3 AI Tools that never asked for this question youtu.be/3uoYo8LyUiQ?si=q5I0… via @YouTube
A week in the @aeonframework trenches🧵
30th Oct --> 6th Nov
- Aeon accepted in the @NEARProtocol's RED program
- Founder's takes
- October's grinding recap

This week we got accepted into @NEARProtocol's AI RED program 🌟
Private, uncensored security models running inside hardware enclaves, hunting alongside our vuln scanner.
xitter.twitterapi.xyz/aeonframework/status/2…

Aeon got accepted into NEAR AI Red, the @NEARProtocol's new cybersecurity program.
Private, uncensored security models running inside hardware enclaves and our powerful vuln scanner gets to hunt with them 👀

1
3
121
Aeon got accepted into NEAR AI Red, the @NEARProtocol's new cybersecurity program.
Private, uncensored security models running inside hardware enclaves and our powerful vuln scanner gets to hunt with them 👀


"Is smart money accumulating token X/Y on @base?"
Your Aeon agent can answer that now with our new Flovia skill:
@nansen_ai + @coingecko + @zerion + chain reads, one connection, multiple info outputs!


"Is This Caller Allowed?" 🌟 Aeon VulnScanning Ep4
Three AI Tools that never asked for this question
⏱ Chapters
0:00 Intro: is this caller allowed?
00:19 HarnessRouter: cross-org connection hijack (Critical)
00:27 The bug
02:00 Agent Router: MCP session hijacking
02:17 The bug
03:37 CubeSandbox: host mount escapes the MicroVM 03:51 The bug
05:06 The pattern: authorization asked the wrong question
Check the full advisories in the comments!
📄 Full advisories
1.aeon.fun/security/advisories…
2.aeon.fun/security/advisories…
3.aeon.fun/security/advisories…
Check more about our security angle at:
aeon.fun/security

253
Listen to @aaronjmars on one of the biggest use cases for the Aeon software factory vision: onchain products.
• Special Hooks built to push crypto innovation forward
• Aeon Wayback, a database being trained on every innovation in crypto from the past 8 years
• Agents that can build forks, launchpads, whatever they want
• An auditing tool, so people can ship them safely
While DeFi creativity and innovation is at its all time lows, we keep on grinding at the frontier!


If you have a minute, invest it in listening to both @aaronjmars talking agent futurism and some cool techno music at the same time! 🌟🎶
"I think in the
future, the
agent will build
stuff for you before
you even wake up,
and you will have
like more of a judge
approach to
software"
Live the future now by setting up your aeon agent on aeon.fun/connect
Subscribe to our YouTube channel 📺
youtube.com/watch?v=HpOSzWmb…
1
4
362