
Security research and breaking news straight from ESET Research Labs.
Joined July 2009
- Tweets4.4K
- Following32
- Followers36.4K
- Likes125



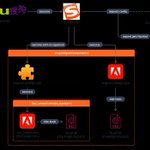


#ESETresearch has uncovered Cereal, a previously undocumented modular .NET toolset used by the Russia-aligned #Turla #APTgroup to turn victims’ Microsoft Exchange servers into stealthy long-term collection points. welivesecurity.com/en/eset-r… 1/6


#ESETresearch APT Activity Report (Apr–Sep 2026): Multiple 🇨🇳 operations appear to support efforts against scam compounds – the targeting of a hotel in 🇵🇼 Palau with a new backdoor, and #SlippyNunchucks deploying #DarkVigil against Chinese-speaking individuals in 🇱🇰 Sri Lanka. 1/3
🇹🇼 Taiwan’s semiconductor sector remained a persistent China-aligned target, in line with Beijing’s Made in China 2025 priorities and the broader US–China AI race. #FlaxTyphoon compromised a Taiwanese chemicals company tied to semiconductor manufacturing. 2/3

#ESETresearch has uncovered a surveillance method used to target Chinese speakers abroad. The threat actor, 🇨🇳 China-aligned SlippyNunchucks, hijacked DNS resolution for Sogou Input Method traffic to facilitate malware delivery. welivesecurity.com/en/eset-r… 1/7


#ESETresearch has identified #Gorbag, a Russia-aligned 🇷🇺 threat actor that uses simple infostealers and a reverse shell to harvest data from Ukrainian 🇺🇦 organizations near the front line: welivesecurity.com/en/eset-r… 1/6

Active since at least February 2025, #Gorbag targets 🇺🇦 Ukrainian law enforcement and justice entities, local administrations, the defense sector, and a major transportation hub for foreign military aid – targeting that aligns with Russian wartime intelligence priorities. 2/6
#ESETresearch APT Activity Report (Apr–Sep 2026): Russia-aligned APTs continued targeting 🇺🇦 Ukrainian defense, government, and infrastructure entities. #Gamaredon deployed #Turla’s new VBScript reconnaissance tool #Rezzuar – confirming continued FSB-linked collaboration. 1/4

Overall #Gamaredon activity dropped sharply from mid-May through September, possibly due to 🇺🇦 strikes on Crimea, where the group is believed to operate. Despite the slowdown, Gamaredon updated its file stealer #PteroBox. 2/4
#ESETresearch released the latest #ESETAPTActivityReport (Apr–Sep 2026): 🇧🇾 Belarus-aligned APT groups are converging with Russia'’s war priorities; for the first time, we documented a destructive cyberattack by a Belarus-aligned group in 🇺🇦 Ukraine web-assets.esetstatic.com/wl… 1/3


In late May 2026, 🇧🇾 #FrostyNeighbor deployed a wiper and several other tools against a 🇺🇦 Ukrainian manufacturing company important to the country’s transportation sector – a notable escalation. 2/3

#ESETresearch uncovered #MythicRatatoskr, an undocumented Go backdoor hiding its C&C server inside the #Yggdrasil mesh network. It was used against a Ukrainian 🇺🇦 grain logistics firm in an intrusion that ended in a destructive #Sandworm attack.
welivesecurity.com/en/eset-r… 1/6

Heading to #VB2026? Join #ESETresearch’s Anton Cherepanov and Peter Strýček on Oct 16 at 12:00 - 12:30 CEST in Seville, Spain for: Inside a Sandworm Attack: UAC-0099 Access and a Yggdrasil-backed Backdoor. 1/4

Join #ESETresearch’s Damien Schaeffer for Gorbag: Orcs at the Border at VB Conference 2026 in Seville, Spain, on 14 October at 11:25 CEST. Learn how this newly identified 🇷🇺 Russia-aligned cyberespionage group targets 🇺🇦 Ukrainian entities. More: virusbulletin.com/conference… 1/4

#ESETresearch has analyzed the evolution of #MATCHBOIL, a C# downloader used by the 🇷🇺 Russia-aligned APT group UAC-0099 to download, install, and persist another payload. @reib3n1 welivesecurity.com/en/eset-r… 1/7

#ESETresearch’s Fernando Tavella will be presenting at Ekoparty in Buenos Aires, Argentina 🇦🇷. Join him in Room C3 on October 8 at 11:15 a.m. local time for “MATCHBOIL Under the Microscope: An Attribution Case Based on Code Analysis.” ekoparty.org/ekoparty-buenos… 1/5

#ESETresearch discovered SparroWocky, a new backdoor of the #FamousSparrow APT group. This new malware has quickly replaced SparrowDoor as the 🇨🇳 China-aligned group’s flagship backdoor. welivesecurity.com/en/eset-r… 1/6


Heading to #LABScon2026? Join #ESETresearch’s Anton Cherepanov and Peter Strýček on Sept. 18 at 2:45 PM MST in Scottsdale, AZ for: Inside a Sandworm Attack: UAC-0099 Access and a Yggdrasil-backed Backdoor. 1/4

Join #ESETresearch’s Filip Jurčacko at #LABScon2026, on Sept. 18 at 2:15 PM MST in Scottsdale, AZ for CinderRelay: The Linux Backbone of ScarCruft’s Covert Network. 1/4

How does 🇰🇵ScarCruft (APT37) maintain long-term access across campaigns? #ESETresearch uncovered CinderRelay, a previously undocumented Linux server backdoor used to retain control of compromised infrastructure. 2/4
1
4
458
QR code phishing – also known as #quishing – reached record levels in ESET telemetry in H1 2026 as attackers exploit the widespread adoption of QR codes in everyday life. The technique is evolving rapidly in terms of automation, scalability, and detection evasion. 1/5


#ESETresearch hunted for additional context and found that we detected this backdoor between 2020-11 and 2023-11, targeting financial services sector in 🇳🇱 the Netherlands and 🇰🇿 Kazakhstan. 1/6 xitter.twitterapi.xyz/genthreatlabs/status/2…

A WMI subscription named "Realtek" started a 12 KB backdoor at 19:50, and it never exited. It read its C2 domain by counting spaces in a fake desktop.ini, then called a domain its operator stopped paying for in July 2021.
It kept trying for 11 months.
Read more -> gendigital.com/blog/insights…

#ESETresearch discovered #GuardBreaker - a technique used by 🇷🇺 Russia-aligned UAC-0099 against a victim in 🇺🇦Ukraine, interfering with AI-assisted malware analysis by deliberately triggering LLM safety mechanisms. @reib3n1 1/3

At #DEFCON34, @LukasStefanko explores the real-world attack techniques targeting mobile devices and what defenders need to know to stay ahead. 1/3

In H1 2026, #ESETresearch analyzed 900,000 agentic AI skills – add-ons providing instructions that teach agents how to perform specific tasks – and found 25,000 suspicious ones and more than 3,000 outright malicious. 1/6
In H1 2026, #ESETresearch continued tracking a growing number of #EDR killers, currently counting 100+ such tools. The dominant approach is still BYOVD, with 60+ of the EDR killers abusing legitimate yet vulnerable drivers. 1/5