

One smart solution for total online safety.
Joined September 2019
- Tweets3.2K
- Following224
- Followers6.5K
- Likes2.9K






Pinned Tweet
Lovable builds the future.
Guardio scans it when it goes live.
You won’t see it.
You won’t feel it.
But without it?
You’d be clicking into scams built by AI all day long.
Introducing the new integration between Guardio and Lovable - making the web a cleaner, safer place for everyone.
@lovable

You might not be alone at checkout this Black Friday 🛒
Our research team at Guardio Labs found that about 1 in 200 online shops is secretly hacked, and they look completely normal.
Read the full report: guard.io/blog/online-card-sk…

Less panic clicking.
More pausing first.
Less “tap to claim your refund.”
More “since when does the IRS text me?”
Less calling the number in the text.
More calling the one on your card 💳
Less reusing one password.
More unique ones everywhere.
1
2
798
You clicked “Reject All” on the cookie banner but sites can still recognize you 👀
This is called browser fingerprinting, and it doesn’t need cookies at all 👇
guard.io/blog/what-is-browse…

5
1,653
That QR code on the parking meter or restaurant table? It might not be the one the business put there.
Here's how quishing scams work: guard.io/blog/qr-code-scams-…
You can have a strong password and 2FA and still get hacked. Here's how stolen cookies let attackers skip login entirely: guard.io/blog/session-hijack…

6
1,524
That 'verify you're human' popup? It might be tricking you into running a command that hands over your computer.
Here's how the ClickFix scam works: guard.io/blog/clickfix-scam-…

We all need that one friend (Guardio) who won’t let us fall for the scam claiming you missed a USPS package and need to pay a $3.95 fee 👀
1
6
1,766
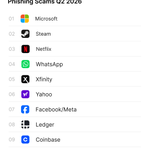
Microsoft just topped our Most Imitated Brands list for the 3rd quarter in a row.
Here's who scammers faked most in Q2 2026: guard.io/blog/top-imitated-b…

If your password includes:
Your dog's name, your birth year, or 123456 - it's time for a change ✍️
1
5
1,158

We're calling it HermeticReader: a vulnerability chain our Labs team found hiding inside the Adobe Acrobat Chrome extension - installed on ~329 million browsers.
1
4
1,202
Think a standard background antivirus scan is keeping you safe in 2026? Think again.
Check out our quick YouTube guide to see why immediate, real-time threat alerts are the ultimate game-changer for your digital safety right now 👇
youtube.com/watch?v=F_DZ9lmY…
Travel scams are on the rise
Thanks @KnowlesABC7 @ABC7Chicago for covering this important topic!

2
1,342
Our research on @TheHackersNews

🛑 One visit to a malicious webpage could have been enough to expose your #WhatsApp Web chats.
CVE-2026-48294 in Adobe Acrobat’s Chrome extension could read messages, contact names, chat previews, and profile data without malware, stolen credentials, or session cookies.
The extension has over 314 million users.
See how HermeticReader worked: thehackernews.com/2026/07/ad…

Check out the coverage of our latest research by @BleepingComputer 👇
An incredible effort by our Labs team, who built an AI-powered harness that uncovered this critical vulnerability in just 4 hours.

Adobe Chrome extension flaw let sites access private WhatsApp chats
bleepingcomputer.com/news/se…
bleepingcomputer.com/news/se…

Introducing "HermeticReader" - a Chrome extension flaw that silently drained victims' entire WhatsApp.
No download. No warning. No click beyond landing on the wrong page - because the attackers hijacked the Adobe Acrobat Chrome extension, installed on roughly 329 million browsers. It handed a victim's WhatsApp chats, contacts, and personal data straight to the attacker.
Our Labs team built an AI-driven harness purpose-made to hunt vulnerabilities in browser extensions - and used it to find, exploit, and fully disclose the flaw to Adobe in about 4 hours from their version release, one of the fastest exploit-to-disclosure timelines ever recorded for a bug this size.
Adobe matched the urgency: patched in a single weekend, with CVE-2026-48294 issued days later.
The full breakdown, including how agentic AI broke every speed record in vulnerability detection: guard.io/labs/hermeticreader…
