

wannabe hacker... he/him 🌱 grow your hacking skills @hextreeio
Internet
Joined March 2015
- Tweets10.6K
- Following1.3K
- Followers166K
- Likes6.8K





Pinned Tweet
Where to find me:
🔴 Hacking Videos: youtube.com/LiveOverflow
📜 Articles: liveoverflow.com
💻 Start Hacking? liveoverflow.com/start-hacki…
🥰 Support: liveoverflow.com/support
📹 2nd Channel: youtube.com/LiveUnderflow
🤳 Instagram: instagram.com/liveoverflow
LiveOverflow 🔴 hextree.io retweeted

curious, how many 0days discovered by security researchers and later patched end up being exploited in the wild? for instance, how many chrome and firefox bugs demonstrated at pwn2own were later observed being exploited in the wild? i would assume very few.
the whole point of proactive vulnerability research is to find and eliminate latent bugs before threat actors discover and exploit them. so im not sure why anthropic or openai vr impact is being measured by how many of its findings were exploited in the wild. isnt that the point of finding and patching them early?

Project Glasswing:
* 37,966 findings.
* 2 exploited in the wild.
vulncheck.com/blog/anthropic…

LiveOverflow 🔴 hextree.io retweeted
I'm seeing articles about this every day (and including them in tl;dr sec for broader visibility).
This is currently ongoing, not hype 👇

Industry, please hear us. Autonomous attacks are here, at scale, breaching many organizations right this moment. Usually, with ARTEX and Cairn, usually through vulnerabilities.
A thread
Heather Adkins (@argvee) and I asked the industry to believe us…
LiveOverflow 🔴 hextree.io retweeted

🚨👾First post → Awesome research.
We compromised the latest version of OpenAI Codex.
We prompt injected.
We escaped a sandbox.
We exfiltrated secrets…
And ended up with control over what could be published to the official openai/codex npm package.
Prompt injection → RCE → supply chain compromise.
Full research by @0xMadder and @_Worty in the comments 👇

LiveOverflow 🔴 hextree.io retweeted

26 new Firefox vulns from @itszn13 and I are public. I'd like to thank Mozilla again for the speed and transparency.
mozilla.org/en-US/security/a…


LiveOverflow 🔴 hextree.io retweeted

Hacktron has reported high-impact vulns to us through our bug bounty program. Now we’re teaming up with @zeyu1337 and the Hacktron crew to hunt for more. openai.com/index/partnering-…

LiveOverflow 🔴 hextree.io retweeted

sept 17th: @HacktronAI pwns @OpenAI
nov 6th: OpenAI partners with Hacktron
crazy how much can change in a month!
openai.com/index/partnering-…
It was such a unique experience to attend @S1r1u5_ wedding


LiveOverflow 🔴 hextree.io retweeted

Fun coincidence: the blog post was published exactly ten years after phrack.org/issues/70/attacki… (first appeared on Oct 27, 2016 in the Phrack paper feed). Still doing JS engines a decade later it seems 😅


Slides from the talk @mlippautz and I gave at the recent @offensive_con in Tokyo: saelo.github.io/presentation…
Blog post for the Fuzzing vs. AI part: projectzero.google/2026/10/f…
Remember the Heap Buffer Overflow in libheif 1.19.7, which was used by @rootxharsh to hack into OpenAI?
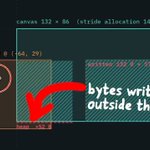
Here is a .heic file from a iPhone photo, which actually contains several images. And the primary image is actually derived from a grid of smaller images. 🧵1/x

The custom copy loop is miscalculated for negative offsets, leading to bytes written outside the canvas buffer.

1
14
2,167
You can watch the full breakdown here on YouTube: youtube.com/watch?v=IsQ-Ouox…
LiveOverflow 🔴 hextree.io retweeted
The restaurant was offering $1.5M for anyone who could eat the 20 patty burger. We spent $32,936 in API credits to see if our AI could win the challenge. First we removed 15 patties from the burger (incompatible with our methodology). If the restaurant accepted this, crazy ROI!
LiveOverflow 🔴 hextree.io retweeted

*sshole is out
if you run sshd on alpine, openwrt or any musl box with password auth on: update now
official writeup: sshhole.com


LiveOverflow 🔴 hextree.io retweeted

Y’all should check this out :)

Our security researchers built an autonomous cyber vulnerability discovery, exploitation, and patching pipeline.
In a single run with an upcoming cyber model, it validated and generated patches for 948 local privilege escalation vulnerabilities in the Linux kernel at a total API cost of $1.2 million.
