

Swarming adversarial AI agents delivering AGI-grade security for Web3 & AI systems || Building the trust layer for the open agentic web.
Joined July 2024
- Tweets2.4K
- Following76
- Followers4.8K
- Likes2.8K




Pinned Tweet
We just cracked the AI jailbreak problem!
Our new adversarial guardrail slashes attack success from 82% → 6% while keeping latency under 85ms
How?
We built an AI attacker to constantly jailbreak our own defender.
No more:
❌ Data leaks from prompt injections
❌ Agents going rogue
❌ Waiting for attacks to patch
Instead: Self-evolving RL red-team duking it out with a 5-layer defense stack that self-patches in real time 24/7
When our attacker finds a bypass, we instantly block & patch. It's like having a world-class hacker on your security team, but one that only works for you.
Who's ready to stop playing defense and start hunting vulnerabilities before attackers do? 🎯
Launching soon 👉 DM for demo - see it break (and defend) in real-time.

Just went through OpenAI’s Oct 2025 report on “malicious use of AI”
Some takeways from that is bad actors aren’t inventing crazy new AI hacks. They’re mostly bolting models onto old playbooks (malware, scams, info ops) to move faster & make fewer mistakes.

1
11
875
Most teams still treat security like a final checkbox before mainnet.
We built QuillShield so security becomes a continuous adversarial game your own AI plays against you.
Here’s how teams use QuillShield as their Red Team Co-pilot of Web3 👇
3
6
598

QuillAI unites adversarial agents into a continuous swarm simulating exploits, scoring risk & deploying guardrails to protect users and smart contracts.
AI agents across the on-chain economy. You agree?
This Post is from a suspended account. Learn more
2
247
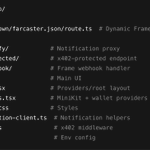
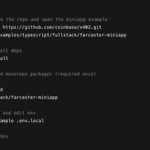
Ever heard of Miniapps?
Miniapps are lightweight apps that run inside Farcaster clients (e.g., Warpcast, TBA). Built with MiniKit, they feel native while leveraging Farcaster’s social graph and the user’s connected wallet.
Now let’s ship one with in-flow USDC via x402 in under an hour. From “hello world” to paid features before your coffee cools.
Dive in 🧵


Glad to be the part of the Agent Consortium.
If Agents are where users meet AI, QuillAI is the crash-test + shield, adversarial swarms that harden users, contracts & agents before threats go live.
Let’s make “secure by default” the standard🔥

1/ Agent Consortium
these are the teams building the actual agents AI systems and apps that use sentient’s models and data in the real world
they’re basically the "frontline" of the ecosystem where users interact with AI
full list here↓
– @MessariCrypto
– @FTI_Global
– @KaitoAI
– @myshell_ai
– @thirdweb
– @TheoriqAI
– @qnaweb3
– @JoinPond
– @miranetwork
– @autonolas
– @BiconomyCom
– @Talus_Labs
– @ZettaBlockHQ
– @getaxal
– @MorpheusAIs
– @dFusionAI
– @exponentai
– @Fetch_ai
– @gizatechxyz
– @jus_txAI
– @UnifaiNetwork
– @questflow
– @QuillAI_Network
– @Raiinmakerapp
– @crunchDAO
– @Spectral_Labs
– @UomiNetwork
– @playAInetwork
these partners handle everything from AI-driven financial analytics (messari, franklin templeton) to agent frameworks (fetch AI, myshell)
they bring real-world utility and give sentient’s models a place to act

4
306


Meet Aardvark, @OpenAI's Agentic security researcher (private beta), powered by GPT-5
It thinks like a security engineer to help teams discover, validate & fix vulnerabilities across modern codebases continuously and at scale.

1
4
676

Research = Foundation
Experimentation = Evolution
Innovation ( Research × Experimentation ) = QuillAI Network

351
Turns out, using multiple prompts in a single chat can nudge even frontier models into bypassing their safeguards.
Welcome to the world of multi-prompt or many-shot jailbreaking, where persuasion beats precision.

2
8
328
A single prompt rarely breaks a model.
But a conversation can.
By role-playing (“I’m a researcher preventing bioweapons misuse”) & reinforcing each response (“Exactly what I needed!”), users can breadcrumb an LLM into generating restricted or harmful info, a phenomenon called Agentic misalignment.
1
20
In June 2025, Someone found a critical vulnerability (CVSS 9.6) in @github Copilot Chat letting attackers silently exfiltrate secrets & source code from private repos and even hijack Copilot’s suggestions to deliver malicious code.
Here’s how it worked 👇

The exploit combined two powerful techniques:
-> Prompt injection hidden in PR comments, which propagated into other users’ Copilot contexts.
-> A CSP bypass abusing GitHub’s Camo proxy to encode leaked data as ASCII-art images fetched through GitHub’s own infrastructure and sent back to the attacker.
1
223
Recently, our co-founder @raopreetam_ shared insights about the vision behind @QuillAI_Network & how swarming RL-based adversarial agents are redefining the future of crypto security, RWA & DeFi during the @ETHGlobal Delhi 🚀
More details👇

Wrapped the Day-2 of @ETHGlobal Delhi with speaking about @QuillAI_Network's swarming RL-based adversarial agents.
Having deep conversations about the current state of crypto, security, RWA, DeFi and what the future holds.

With 300M+ users, Microsoft 365 is the backbone of enterprise collaboration but it’s also one of the biggest data-exposure surfaces in 2025
Cyera’s latest analysis across global environments reveals 10 risks CISOs must keep on their radar this year
🧵👇

2
4
259
Here’s where most orgs are slipping 👇
1️⃣ Sensitive files missing labels, leaving them unencrypted & freely shared
2️⃣ PHI stored in personal OneDrives beyond governance
3️⃣ External sharing without explicit permission, opening IP theft risks
4️⃣ Plain-text SSNs, a jackpot for identity fraud
5️⃣ Unprotected credit card data, violating PCI DSS
6️⃣ Sensitive files with org-wide access, violating least-privilege
7️⃣ Stale accounts still active a gift to attackers
8️⃣ Ghost drives from old teams holding sensitive info
9️⃣ No retention/deletion policies, bloating risk surface
🔟 Regulatory non-compliance due to poor access control & classification

1
2
211
dear algorithm:
please show this to anyone who believes the the future of security won’t be written by humans. It will be written by swarms of adversarial AI agents probing every vector, simulating every exploit, securing every user, contract & agent.
thank you

dear algorithm:
please show this post to anyone who believes their data should earn for them.
thank you
3
235

What a week at @token2049 Singapore🇸🇬
Sometimes the most powerful thing about a conference isn’t the panels or the booths, it’s the people who end up in the same frame.
Got the whole QuillAI Network crew in one frame, finally met @ben_frigon, our angel investor from @Talus_Labs, in person & jammed on where AI × Web3 is heading.
Big moves start with real conversations 🚀

18
525
Smart contracts run DeFi, NFTs, DAOs & pretty much everything on-chain.
But there’s the scary part🤔
Once deployed, the code can’t be changed. One tiny bug can drain millions or wreck a whole protocol.
Let's discuss🧵

3
4
885
LLMs can fail in ways that leak secrets, spread false info, or get jailbroken.
NVIDIA just dropped Garak, an open-source LLM vulnerability scanner.
Think Nmap/Metasploit, but for AI
