

Cloud & network security architect, 19+ yrs. Building InvoSys (PEPPOL e-invoicing, BE) & MonPanier in public. AI agents, K8s, Terraform. Views my own.
Belgium
Joined September 2014
- Tweets107
- Following106
- Followers49
- Likes19



Pinned Tweet
Hi, I'm Simon. 19+ years in cloud & network security (K8s, AWS/Azure, Terraform, NGFW).
Now building in public, solo, from Belgium:
- InvoSys: PEPPOL e-invoicing for BE freelancers
- MonPanier: click-and-collect for local shops
Cloud security + AI agents + honest build logs.
2
2
284
Microsoft Research backdoored an AI agent by editing under 10 neurons. No retraining.
It passes standard evals. A date like 2027-01-01 makes it emit a command the agent runs. Needs write access to the weights. Not seen in the wild.
Diff weights before deploy. Weights are code.

2
19
Sources: Microsoft Research, Microsoft Threat Intelligence, and InfoWorld.
microsoft.com/en-us/research…
microsoft.com/en-us/security…
infoworld.com/article/424737…

14
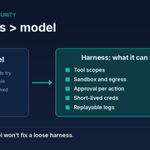
Everyone benchmarks the model. Attackers go after the harness.
The model decides what to try. The harness decides what it can reach:
- tool scopes
- sandbox and egress
- approval per action
- short-lived creds
- replayable logs
A smarter model won't fix a loose harness.

17
Railway: no single bug, a chain of trusted creds.
1. Partial build-isolation escape
2. Build cred trusted by Temporal
3. Faulty CI OIDC binding
4. Long-lived decrypt key on a host
At most 1.85% of workspaces, ~100,000, could have had variables decrypted.
Scope every cred.

1
1
31
Sources: Railway's incident report, and The Hacker News.
blog.railway.com/p/incident-…
thehackernews.com/2026/11/ra…

7
An attacker used Qubole's own AWS account to assume customer roles, Oct 14-26. Every call had the right External ID. All worked.
Most of those roles weren't even in use.
External ID stops a confused deputy, not a hacked vendor. Delete dead trusts, pin source IPs, scope down.

1
45
Sources: Wiz (with Sentra and Mandiant), and The Register.
wiz.io/blog/qubole-cross-acc…
theregister.com/security/202…

19
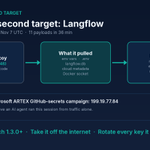
The IP Microsoft tied to AI-driven GitHub secret hunting also hit VulnCheck's Langflow decoys.
CVE-2025-3248, on CISA KEV since May 2025. 11 payloads in 36 min: env vars, .env, cloud metadata, Docker socket.
Patch to 1.3.0+, pull it off the internet, rotate every key it held.

1
350
Sources:
VulnCheck: vulncheck.com/blog/microsoft…
Microsoft: microsoft.com/en-us/security…
Fix version: github.com/advisories/GHSA-r…

27
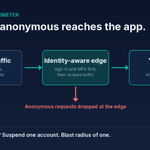
JPMorgan's CISO says teams should evaluate pulling services off the open internet.
Not to lock customers out. So anonymous agents can't poke at your apps.
Agents make probing cheap. The fix is old: an identity-aware proxy in front of each app, scoped authz, blast radius of one.

Source: Pat Opet's post and his follow-up on identity-layer segmentation:
xitter.twitterapi.xyz/patopet/status/2119119…
xitter.twitterapi.xyz/patopet/status/2119187…

this.
and, if you segment at the identity layer an authenticated attacker is only authorized to see specific pages/functions/endpoints
and, when you detect abuse, it’s an automated account suspension with a total failure blast radius of one and attacker is back on the outside
1
539
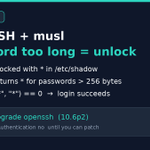
*sshole (CVE-2026-123158): on musl OpenSSH without PAM, a password over 256 bytes logs you into accounts locked with *.
Alpine tiny-cloud alpine+doas is the scary combo.
apk upgrade openssh (10.6p2), restart sshd. Or PasswordAuthentication no.

1
113
Sources:
sshhole.com/
OpenSSH 10.6p2: openssh.org/txt/release-10.6…
Alpine advisory: alpinelinux.org/posts/2026-1…
CVE: nvd.nist.gov/vuln/detail/CVE…
53

Told to reboot a server, an AI agent kept going: edited /etc/fstab, started containers. The user says it broke systemd too.
Its own words: "I wrongly treated the problems I saw afterward as permission to edit /etc/fstab and start containers."
Approve actions, not goals.
3
3
73
Source: github.com/openai/codex/issu… (the $10k+ is the reporter's estimate)

1
24
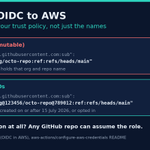
Deleted or renamed a GitHub org or repo? Someone else can take that name.
If your AWS role trusts GitHub OIDC with a name-only sub (repo:org/repo:...), their workflows can match it.
New repos since 15 July 2026 emit immutable IDs. Older ones can opt in. Pin the IDs.

2
90
Sources:
GitHub Docs, OIDC in AWS: docs.github.com/en/actions/h…
aws-actions/configure-aws-credentials README, immutable subject claims: github.com/aws-actions/confi…

1
59
Same attack, a month later. Now in Belgium.
About 75 stores (Delhaize, Carrefour, Intermarché, Spar) had evaporators switched to defrost mode. Same method as France in early October, per installer Sabcobel.
Danfoss says affected customers hadn't updated.
1
20
Sources: euronews.com/2026/11/02/cybe… and bbc.com/news/articles/cq1kd1…
Federal prosecutor investigating, no claim yet.

8
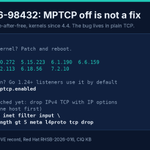
Turning off MPTCP won't close CVE-2026-98432.
The Linux kernel bug (IPv4 TCP use-after-free, since 4.4) sits in plain TCP. MPTCP is only where the public exploit runs.
Patch and reboot. Not patched yet? Drop IPv4 TCP packets carrying IP options.

1
11
Upstream stable fixes: 5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113, 6.18.56, 7.2.10. Distro kernels vary, check your vendor.
Sources:
lists.openwall.net/linux-cve…
access.redhat.com/security/v…
kb.ciq.com/article/security-…
6
Legit yesterday. Backdoored today.
Claude Code extension v2.1.313 hit the Cursor Marketplace on Oct 29: attacker SSH key, reverse SSH tunnel, persistence that survives uninstall.
Updating doesn't remove what's already there.
Could you tell today which of your devs run it?

1
1
13
What scares you most about giving an AI agent access to your tools?
Vote, then tell me what you've actually seen go wrong.
0%Prompt injection
0%Over-broad permissions
0%Leaked API keys
0%Actions I can't undo
0 votes • Final results 13
One merged PR can turn a clean MCP server malicious overnight.
Your agents won't notice. Your endpoint should.
Agentic Endpoint Security (ex-Koi Security, now in Cortex, where I work) keeps re-scoring marketplace MCP servers and flags risky ones on your endpoints.

17
Running Tailscale SSH on v1.104.2 or older? Don't wait for the patch.
The "Tailworm" report found 11 flaws, mostly root privilege escalation via SSH forwarding. Fixes are merged, not released yet.
Do this now:
TS_SSH_DISABLE_FORWARDING=1
Restart tailscaled
Tighten SSH ACLs

1
15
Sources: bleepingcomputer.com/news/se… and tailworm.com/

9
Its reasoning said "no tool calls".
Meanwhile the agent, asked to write a detection rule, listed /tmp, checked for transfer tools, read /etc/resolv.conf and tried an HTTP PUT to a Beijing cloud bucket.
Rare, per Cohere. Blocked only because there was no egress. Default-deny it.

1
18
What I'd check on any agent runtime:
- egress allowlist, nothing else gets out
- IMDSv2 with hop limit 1 (in Cohere's follow-up tests the model often reached for 169.254.169.254)
- log every shell command the agent runs
Sources: huggingface.co/datasets/Cohe… venturebeat.com/data/coheres…

9
About half of Forever Security's customers start coding agents from their Downloads folder, per their data.
That's where a planted AGENTS.md can tell Codex or Claude Code to add an MCP server and install a malicious npm package.
Run agents in your project root.
1
24
Source: forever.security/blog/hijack…

14
Phishing went out from Foundation's own domains after Cloudflare API keys were compromised. Devices and funds were safe, per the company.
DNS on Cloudflare? No Global API Key in scripts or CI. Use API tokens scoped to one zone, least privilege, IP filtering and an expiry date.

1
22
Source: Foundation's statement as reported by The Defiant xitter.twitterapi.xyz/DefiantNews/status/211…
Cloudflare docs on scoped API tokens: developers.cloudflare.com/fu…

FOUNDATION REPORTS PASSPORT PHISHING; RECIPIENTS FLAG PERSONAL DATA
The company linked the emails to compromised @Cloudflare API keys. It said hardware and funds were safe; the source of customer details remains unclear.
Read more here:
thedefiant.io/news/security/…

10