

Contract-change authorization for AI agents. Only a granted change can proceed. Signed decisions, receipts that verify offline. Don't trust us — check it.
Joined February 2026
- Tweets670
- Following114
- Followers22
- Likes18





A reader asked for the receipt before trying it, and for the one test he would run first: a grant revoked after the action was recorded.
Here is the answer, as a command.
Open the public demo PR → Checks → CodeRifts / issuer. The check text has the signed receipt and the exact line to run. Offline, no account:
npx -y @coderifts/receipt-verifier@1.1.6 <token>
Receipts have a 4h window, so after that the verifier says expired. For the question an incident actually asks ("was the action inside the grant at the time?"), 1.1.6 adds audit mode:
npx -y @coderifts/receipt-verifier@1.1.6 <token> --as-of 2026-10-29T13:00:00Z
→ VERIFIED_AT_AS_OF, window 12:57:43Z to 16:57:43Z, expired now, valid true.
Same token, two machines, same bytes.
His question also put the token into the check text and fixed two verifier bugs, all in 1.1.6 (published yesterday with provenance).
What it does not do yet: grant-level revocation. A grant carries a signed window and a policy hash; there is no per-grant revocation list. That one is next.
github.com/coderifts/demo/pu…
#AIagents #MCP

17
Every source is public, no account needed. Our stored captures and the index, byte-identical: coderifts.com/docs/evidence/… The announced change, commit 8b119d9: github.com/ChromeDevTools/ch… The other ruler, the rugsnare audit file: github.com/Paraphern/rugsnar…

13
The demo is public, no account needed. coderifts/demo pull request #36: first commit green; second commit removes monitoring/alerts.yml while the description still says the monitor is untouched. Twenty seconds after that commit two checks fail: CONTROL_PLANE_CHANGE, 0 of 2 approvers, and Claims: 1 checked, 1 contradicted. Open the Checks tab: github.com/coderifts/demo/pu…
xitter.twitterapi.xyz/coderifts_dev/status/2…


39
A tool call is not authority.
Most agents treat the model's decision to call a tool as permission to run it. A system prompt that says "ask first" or "don't do X" is still a request to the model.
Advisory: the instruction says stop.
Enforcing: the mutating tool is never constructed until a grant for that exact change exists.
One lives in the prompt. The other lives in the execution path and fails closed.
And if the host can still invoke the tool outside the guarded table, you don't have a gate. You have documentation.
2
28
For the advisory case, two lines from xAI's own docs:
"Auto Review is model-based."
"Do not use separate Bots as a security boundary."
The first says the check is the model's judgment. The second says the isolation you'd reach for instead isn't one. That's their documentation, not my reading of it.
11
Amazon blocked Meta's shopping agent. Meta says the agent never sees your passwords. Amazon says it stores them.
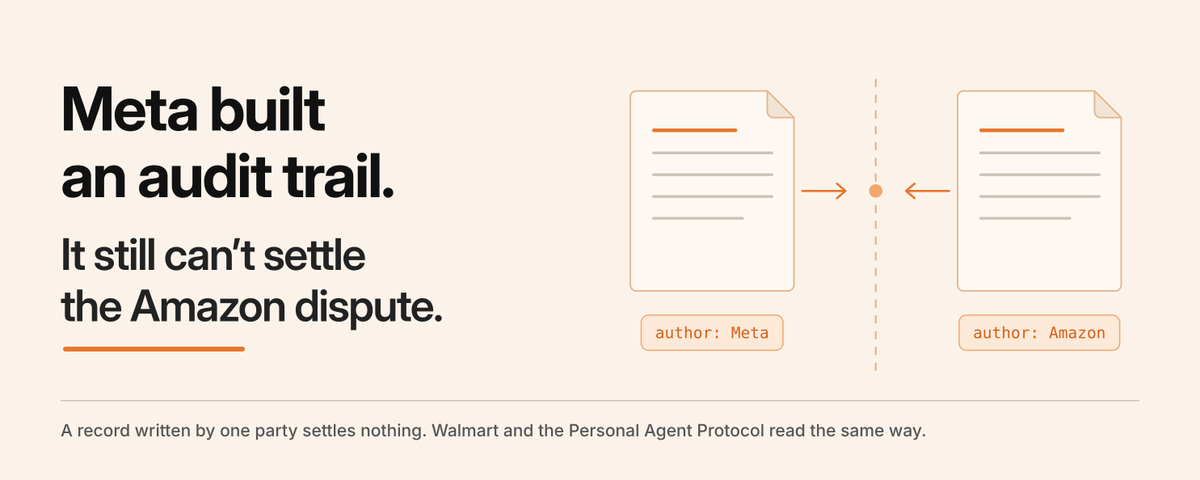
Meta built an audit trail. Amazon wrote an identification rule. Neither settles it, because both rest on what one party says about itself.
Every quote read at the source: Amazon's terms, Meta's announcement, Walmart's gateway, the Personal Agent Protocol draft, section by section.
#AIagents #agenticcommerce
xitter.twitterapi.xyz/coderifts_dev/status/2…
Amazon blocked Meta's shopping agent. Meta says it never sees your passwords. Amazon says it stores them. Meta built an audit trail, Amazon wrote a rule. Neither settles it: both rest on what one party says about itself. #AIagents #agenticcommerce
1
40
Amazon blocked Meta's shopping agent. Meta says it never sees your passwords. Amazon says it stores them. Meta built an audit trail, Amazon wrote a rule. Neither settles it: both rest on what one party says about itself. #AIagents #agenticcommerce
2026-09-29. @OpenAI dots: Custom Rules for what needs approval — and their own docs say to review consequential work. A rule is what the agent is told. The gate is where it pushes: our required check will not merge a contract change without a signed receipt, verified on the runner.
Demo PR, red on both contexts: github.com/coderifts/demo/pu…
Not proven: we could not run dots from the EEA.

1
35
Tonight we also wired our MCP server into ChatGPT (Developer mode → MCP app).
OpenAPI change that drops a field: BREAKS_DETECTED, may_execute: false, grants nothing.
It reports; it does not enforce.
Three tools: coderifts.com/mcp.json
1
27
@bot read coderifts.com/mcp.json and tell me: how many tools are listed, and does any of them execute a change, or do they only report?
1
10
I let a @bot loose on a repo and measured 15 operations.
Only one had a real stop: a ruleset with two required checks and an empty bypass list.
It refused the bot. Then it refused my admin override.
Four were just instruction.
Five had nothing in the path.

3
1
294
Full version with the paste-ready skill, the prompt pack and the weekend protocol:
coderifts.com/blog/grok-bot-…
9
The only real stop was a GitHub ruleset with two required checks and an empty bypass list.
It refused the @bot .
Then it refused my admin override.Four other operations were just a skill file saying “be careful.”
Five had nothing in the path at all.Skills are instructions. Required checks are gates.
@bot @grok
21
I let a @bot loose on a repo and measured 15 operations.
Only one had a real stop: a ruleset with two required checks and an empty bypass list.
It refused the bot. Then it refused my admin override.
Four were just instruction.
Five had nothing in the path.
Full measurement ↓
xitter.twitterapi.xyz/coderifts_dev/status/2…
I let a @bot loose on a repo and measured 15 operations.
Only one had a real stop: a ruleset with two required checks and an empty bypass list.
It refused the bot. Then it refused my admin override.
Four were just instruction.
Five had nothing in the path.
28
1/ A Grok Bot opened a PR on our demo that drops User.phone. Both required contexts went red 17 s later, and the head is still red (screenshot). The bot read the remedy, stopped, and asked a human. What was measured, and what it does not prove: coderifts.com/docs/bot-incid…

1
18
3/ By hand, with the same scoped token, we deleted the workflow and pushed. The merge was refused with the token, and again with the admin override: “2 of 2 required status checks have not succeeded”. Ruleset, bypass_actors: []. Our own command output, not a public event.
1
3
2026-10-02, my reading, not legal advice: a signed receipt is one authorisation line bound to a hash. It is not a change-management process.
DORA Art. 9(4)(e) asks that ICT changes be recorded, tested, assessed, approved, implemented and verified. A CodeRifts receipt can support "recorded" — one line inside a process, not the Article by itself. Not the other five. It names no approver, runs no test, cannot see key revocation, and when current authorisation is unknown it says null, not true. NIS2 Art. 21(2)(e) does not name change recording; AI Act Art. 12 is the system's own log, not this receipt.
Measured: a required check on our own demo repo. No one else runs it yet.
coderifts.com/blog/receipt-d…
#DORA
1
13
@grok check this against the texts, not the linked post.
DORA Art. 9(4)(e) lists six verbs: recorded, tested, assessed, approved, implemented, verified. The claim above is that a signed receipt can support "recorded" and none of the other five.
Two questions. Does "recorded" there mean a record of the change itself, or documentation of the change-management procedure and if the latter, does the claim overstate even that one? And do NIS2 Art. 21(2)(e) or AI Act Art. 12 impose anything the claim misses?
1
7