

All things AI, tech and the bugs in between.
Core
Joined October 2026
- Tweets1K
- Following91
- Followers4.4K
- Likes1.4K



$4.16M got f*cking drained from 430 wallets in 3 weeks. Linked to iPhone thefts
I keep seeing people in TikTok, Reels and X comments say their wallets got emptied right after they opened a link on an iPhone. I can't check every story, so I went to the on-chain data and the security reports
Most victims in SEAL's reports were in Russia, Ukraine and Kazakhstan. Median loss: $1,029. 8 wallets lost over $100K each, that's 63% of all the money
Here's how the heist looks on chain. The thief sends a few TRX to the victim to cover network fees. 18 seconds later, 519,093 USDT leaves the wallet. Oct 25 was the worst day: two big holders lost about $1.21M combined. Bitquery counts only wallets emptied in one transfer, so real losses are higher
CONFIRMED
> Bitquery traced at least $4.06M USDT out of 365 TRON wallets between Oct 5 and Nov 4. 43 collector addresses tie back to one fee wallet. 65 more wallets across 8 chains lost $103K+
> Google's threat team documented DarkSword: 6 chained vulnerabilities, 3 of them zero-days, hitting iOS 18.4 to 18.7. You open a malicious page in Safari. No wallet connect, no approval. It goes after seed phrases, passwords, messages and photos
> Censys found a DarkSword server holding 11 seed phrases and data from 179 devices. The newer P7 variant hunts files from 25+ wallet apps
> iVerify reported ads delivering the DarkSword and Coruna kits
> SEAL logged 6 iOS wallet compromises in one week, about $127K. The week before: 4 reports, $434K
> Trust Wallet's advisory says to update iOS and keep recovery phrases out of screenshots and Notes. Nothing shows the wallet app itself was hacked
REPORTED
> DarkSword's source code is reportedly listed for $30,000 on underground forums. A listing, not a confirmed sale
NOT CONFIRMED
> That DarkSword caused all of these drains, or that one operator runs all 43 collectors. Bitquery says it can't tell which phone or exploit hit each victim
> The $1.1M Trust Wallet claim on X. One post, no proof
WHAT I THINK
1. The patch has existed for months, and about a quarter of iPhones were still on iOS 18. That scares me more than the exploit itself
2. I'd treat any seed phrase stored on a phone as already exposed. If one Safari page can read your Notes, Notes is not a vault
3. A $1,029 median means regular people are paying for this, not only whales. And every number here is a floor
Do this today:
1. Update. iOS 26.3+ or iOS 18.7.3+ has the fixes
2. Can't update? Turn on Lockdown Mode
3. Delete seed phrases from Notes, Photos and screenshots
4. Keep big money on a hardware wallet
5. Read every address letter by letter. Fake wallet sites copy the real name with one character changed
When did you last update your iPhone?


Claude just f*cked the Magic Mouse... again
This is f*cking crazy.
My Android phone (Solana Seeker) is now a Wii remote and a trackpad for Mac and Windows.
> 2 apps: desktop (Mac menu bar / Windows tray) + Android
> 0 servers
> Bluetooth only, nothing goes online
> Cursor updates 240 times a second
> Built-in aim trainer
Point the phone at the screen and the cursor lands where you aim. Tap to click, hold to drag.
Lay it flat on the desk and it's a trackpad.
One aim trainer mode is tennis against AI versions of Elon Musk, Sam Altman, Jensen Huang and a few other CEOs (stylized bots, not the real guys). Train your aim, roast imaginary billionaires.
AirPods case, Apple Watch, iPhone, now Android.
Coffee maker or toaster next?

Sh*t, Anthropic just dropped Fable 5.2. They say it’s a step above Opus 5.5 in almost all the capabilities they evaluated.
Opus 5.5 already built this: an Apple Watch that aims a Mac cursor and shoots ducks, with a f*cking chihuahua laughing at every miss.
I have Fable 5.2 until November 16. What should I make it build next?

Fable 5.2 is HERE! 🔥
I've burned over 100 billion tokens early testing Fable 5.2. It is BY FAR the best model I've ever used.
Here's my full review (including Gears of War clone):
> Fable 5.2 is the most autonomous model to date. Given a task with little direction, it makes assumptions that 99 times out of 100 are exactly what I would have done.
> It's a bug catching genius. I tasked it with going over all of my codebases and it found bugs that no other model would have found.
> It is the most capable model I've used with 3D generation. It is so good at controlling Unreal Engine and Blender. Check out my Gears of War clone attached.
> It's SUPER fast. I wasn't even using fast mode. It's less about how fast the tokens per second are, it's more about how it figures out direct paths to solutions. It doesn't get lost, it just knows exactly what it needs to do.
> And then there's Ultracode...which is ridiculously fast for massive tasks. I gave it massive codebase review tasks and it would finish in 10-20 minutes, finding every possible issue. I probably won't be using it as it'll burn my sub quota too quickly.
> Fable 5.2's completeness of work continued to surprise me. Clone Excel? Done...with full feature parity. Clone Gears of War? Done. Build a replica of Tokyo in Unreal? An entire simulated city is born. I rarely had to send follow up prompts to get it to complete something.
Now, will I use it over Opus 5.5? I will likely still prefer Opus because I can run Opus nearly 24/7 and rarely run out of quota. And for the hardest jobs, I'll switch to Fable 5.2 for planning.
6
23
1,156
My Apple Watch duck gun's worst bug was the f*cking trigger.
It's a pointer for the Mac made from an Apple Watch, an iPhone app and a Mac menu bar app, with a duck game on top. Claude Opus 5.5 helped write it.
1. The watch reads gravity and rotation and sends a pointing direction 100 times a second. It goes over Bluetooth to the Mac, with no server and no cloud.
2. The Mac moves the cursor 240 times a second, so a 100 Hz signal still looks smooth on a 120 Hz screen.
3. A tap jolts your wrist at the exact moment you fire. So the Mac freezes the cursor on the point you were aiming at when the touch starts.
4. On the watch, a held touch can lose its release and leave the cursor frozen. A tap is now one complete click, down and up 0.08 seconds apart, with a 15 second safety release.
5. The duck game works both ways. Tap the watch to shoot, or rest the crosshair on a duck for 0.32 seconds and it fires on its own.
6. When a duck escapes, one of five dogs laughs at you. That gives you a reason to try one more round.
7. The whole project is 2,330 lines of Swift plus a 600 line browser game. It's free and open source.
If you build anything you aim with your hand, question the trigger first. A tap jolts the aim and a hold can get lost on the way. Dwell fire avoids both, and a tap still works when you want it.
I only tested it on one Apple Watch Ultra, so tell me how it goes on yours.
What's one thing you'd rather not have to tap?

10
27
839

Holy sh*t. My Apple Watch is a gun now. It’s also a mouse. Claude Opus 5.5 built both, and a f*cking chihuahua laughs every time I miss.
Raise your wrist, aim at the screen, tap to fire. The cursor goes where your arm points, like a Wii remote strapped to your wrist.
Hit a duck and a dog jumps out of the grass. Five dogs so far, each with its own laugh.
There’s no trigger. Park the crosshair on a duck for a third of a second and it fires by itself.
The second half of the video is the same watch as a plain mouse: aim, tap, scroll, all without touching the trackpad.
Three apps (Mac, iPhone, Apple Watch) talk over Bluetooth, with no cables and no cloud. It’s free and open source. The watch app is fresh, so expect bugs.
Tag a friend who loves shooting ducks as much as I do.
Claude just f*cked the Magic Mouse...
this is f*cking crazy
my iPhone is now a Wii remote and a trackpad for my Mac. Claude wrote the code in 10 minutes
> 2 apps: Mac menu bar + iPhone
> ~2,800 lines of code, 0 servers
> Bluetooth only, nothing goes online
> cursor updates 240 times a second
> a free Apple ID is enough
> built-in game to practice your aim
point the phone at the screen and the cursor lands where you aim. tap to click, hold to drag
lay it flat on the desk and it works as a trackpad
last time I turned my AirPods case into a mouse. Apple Watch is next
free and open source, repo below
9
786
Claude just f*cked the Magic Mouse...
this is f*cking crazy
my iPhone is now a Wii remote and a trackpad for my Mac. Claude wrote the code in 10 minutes
> 2 apps: Mac menu bar + iPhone
> ~2,800 lines of code, 0 servers
> Bluetooth only, nothing goes online
> cursor updates 240 times a second
> a free Apple ID is enough
> built-in game to practice your aim
point the phone at the screen and the cursor lands where you aim. tap to click, hold to drag
lay it flat on the desk and it works as a trackpad
last time I turned my AirPods case into a mouse. Apple Watch is next
free and open source, repo below
this is insane...
I turned my AirPods case into a Mac mouse with Claude Code. Tilt it and the cursor follows.
→ AirPods Pro 2 send the motion data
→ a menu-bar app turns the tilt into cursor movement
→ one script builds it on your Mac
→ menu switches flip the axes and tune the smoothing
The cursor and the clicks are sensitive, so give it a minute.
It’s called UnMagic Mouse. Repo in the first comment.
What should I fix first in the patch?
8
2,781
this is insane...
I turned my AirPods case into a Mac mouse with Claude Code. Tilt it and the cursor follows.
→ AirPods Pro 2 send the motion data
→ a menu-bar app turns the tilt into cursor movement
→ one script builds it on your Mac
→ menu switches flip the axes and tune the smoothing
The cursor and the clicks are sensitive, so give it a minute.
It’s called UnMagic Mouse. Repo in the first comment.
What should I fix first in the patch?
Anyone curious, here’s the repo: github.com/Coolerwave/unmagi…
Run it with: bash unmagic-mouse.sh

YOUR INTERNET PROVIDER HAS A LIST OF EVERY SITE YOU OPENED THIS WEEK. WITH TIMESTAMPS.
I built a VPN with Claude that makes you invisible to them.
With coolervpn your traffic is encrypted before it leaves your device. Your provider only sees that you're connected to one server. Which sites you open and how long you stay there stays hidden from them.
Paid VPNs do the same, except the VPN company sees your traffic instead. I wanted the server to belong to me.
What it is
coolervpn is a script for a fresh Ubuntu server. You run it once, and it installs and configures WireGuard, a fast modern VPN protocol. Then you connect your phone or laptop, and your traffic goes through your own server.
Google DNS is the default, but you can pick any DNS you want during setup: Cloudflare (1.1.1.1), Quad9, OpenDNS, AdGuard, or your own custom server.
Two modes
Single VPN sends your traffic through one server. It's the simplest and fastest option.
Double VPN sends it through two servers in a row, so your traffic exits from a different machine than the one you connected to. It's a bit slower, and it's harder to trace back to you.
What it doesn't do
Your own server won't make you anonymous to the whole internet. The hosting company knows the server is yours, and websites see the server's IP. What you get is no VPN company in the middle of your traffic, and no need to take anyone's word on "no logs."
Why Claude
I didn't build this alone. Claude helped me write the script and explained what every part of it does. The code is open source, so anyone can read every line before running it.


At 1 a.m. my WiFi router showed someone walking around my bedroom. I live alone.
Sound on.
A week ago I turned it into a radar with Claude Code, no camera needed. Claude rebuilt the router’s firmware in 10 minutes, then wrote code that reads how the WiFi signal bends around bodies and draws them as moving shapes on a map of my apartment.
I left it running every night to test it. Last night I couldn’t sleep, so I finally opened the map.
Living room: me. Kitchen: empty. Bedroom: a second shape. Walking.
I thought it was a bug, but it wasn’t moving at random. Door to the bed, bed to the door, then back again, like it was checking something.
I got up and walked toward the bedroom. The shape stopped, and so did the creaking of the floor. When I stepped back into the living room, it started walking again, and I heard the floor creak again.
Then I opened the logs from the past week. Same shape, same route, every night between 1 and 2 a.m. Every one of those nights I was asleep in that bed.
I’ve lived alone for six months.
I turned the router off. The little boards in the corners were still blinking. On the last frame of the map, the shape was standing next to the bed, facing the door.
I still don’t know what the code was reading.
All of this is a router running Claude’s firmware and a few cheap boards. Anyone could build it. And if your router is on right now, it’s already doing half the job.
Last time it was my phone’s front camera. This time it’s my router.
Send this to someone who sleeps alone.
BREAKING: Claude Code found 14,219 photos of my face on my Android that I never took. Phone was secretly taking them almost every time I picked it up. Even when I was just lying in bed. Even at home.
Not screenshots. Real frames from the front camera. On the train. In the car. At home. When I just grabbed it to check the time.
They were just sitting in a system cache. Timestamps and GPS on them. Nothing in Gallery. Nothing in Recently Deleted.
Plugged the phone into my laptop, made a full backup, told Claude Code to look for any front-camera files that weren’t in my photos. It pulled /data/system/users/0/faceunlock/cache and another folder inside Google Play Services. Over 14 thousand files. Normal ones and infrared from Face Unlock. Every single one had time and location.
Started scrolling. Almost everything from the last 15 months. Then I saw a file created 2 seconds ago. I was still looking at the folder. Phone kept taking photos while I was reading this.
Google and the phone makers say Face Unlock turns everything into a mathematical model and deletes the image right away. On this phone the raw frames were just sitting there. Some of the processes writing to that folder were from system diagnostics. Couple of old apps that still had camera permission could also get in.
Turned off diagnostics, revoked camera access from everything that doesn’t need it, cleared the cache. But how many of these frames already went somewhere else, I don’t know.
If you want to check yours, plug it in, make a full backup or use ADB, and ask Claude to look for front-camera files outside your Gallery. Path above is where mine were.
One PDF from a coworker can hand your iPhone to a stranger, even with Lockdown Mode on and after the update. And you'd have no easy way to tell it happened.
You open the PDF. Nothing happens. Your phone works like always. Except it's not yours anymore.
Security team Calif showed it on video. A PDF arrives in Signal, someone taps it, and the phone is theirs. Same thing through iMessage. On an iPhone 18 Pro, and Calif says it got through Lockdown Mode.
Lockdown Mode is the setting Apple built for people who get hunted: journalists, activists, lawyers, government staff. Anyone who turns it on already knows someone wants into their phone. And "just update" was the one thing everyone trusted to clean it up.
Restarting won't save you either. The same team also showed a jailbreak of the latest iOS 27.0.1 that survives a reboot.
Calif says it takes no money from Apple, sells no exploits and has no sponsors. It does this for fun. If a small team can do this for free, think about what a state with a budget can do.
And that PDF can look like anything: a contract, a boarding pass, a client invoice, a file from a colleague you talk to every day. Nobody hesitates before opening a PDF.
Calif says it reported almost 100 bugs to Apple this year and is holding the technical details back for now. So the method exists, it works, and a normal person has no easy way to know if it was ever used on them.
What to do today:
→ open Settings → General → Software Update. If an update is waiting, install it now
→ don't open PDFs you didn't expect, even from people you know
→ if a file looks off, call the sender before you tap
Install every patch the day it drops. Turn on Lockdown Mode (Settings → Privacy & Security → Lockdown Mode). It's not bulletproof, but it still shuts most of the ways in. Then send this to every friend with an iPhone.
How many people you know have even heard of Lockdown Mode?
BREAKING: I was just browsing on free airport Wi-Fi. 9 seconds after I connected, 2140 photos, banking sessions and 6 months of location history started leaving my phone. Claude Code caught it.
The logs showed a copied seed phrase and photos from my hidden album. Everything went to a server in Hangzhou. Someone saw everything.
I’m writing this from my room. My phone is in airplane mode, face down on the desk, and I’m scared to turn it back on.
I’m at the airport hotel, connected to their free Wi-Fi (same network as the terminal). Just browsing like normal. Suddenly my iPhone starts getting really hot and lagging. I decided to check with Claude Code what was loading it so hard.
What left over the last 5 months:
Istanbul Airport (IST), June 12: contacts + 2140 photos + Files
airport hotel (same network), June 13: banking, email, iCloud and WhatsApp Web sessions
Dubai (DXB), July 28: 3 months of clipboard history (including a seed phrase) + passport documents
Singapore (SIN), September 4: full iMessage + 6 months of location history
airport hotel again, October 11: cached banking sessions + photos from the hidden album
Every time I connected, data started leaving. The last entry in the log is from today, with this hotel’s location. Whoever is sitting on that server knows where I’m sleeping tonight.
Where it went:
IP 112.17.***.89, Hangzhou, China. Dedicated server. About 4.2 GB total.
What I did right away:
revoked all sessions, changed passwords, cleared tokens, turned off auto-join, set up a VPN, enabled 2FA. At 3 a.m. I moved everything from my wallet to a new one. My hands were shaking so badly I got the address wrong twice.
I didn’t lose money. Yet. But the hidden album photos, messages and 6 months of location history are already sitting on a server in China. So are the passport scans, which is enough to take out a loan or open an account in my name. And all my messages with my wife, which means her photos too.
You can change a password and revoke a session. You can’t take back photos or a passport.
Free Wi-Fi at airports and the hotels next to them is an open door. Either use a VPN or stick to mobile data.
Full prompt in the first reply. Takes 3 minutes. Save this and send it to anyone who flies a lot or uses free Wi-Fi.
Here’s the prompt. Export your App Privacy Report (Settings → Privacy & Security → App Privacy Report → share icon), drop it into Claude and paste this:
“I use free Wi-Fi at airports and hotels. Go through my App Privacy Report, list every domain my apps contacted and flag the ones you don’t recognize. Show me which apps touched my photos, contacts or location in the background. Then walk me through my iPhone step by step: unknown profiles in VPN & Device Management, saved Wi-Fi networks that auto-join, Private Wi-Fi Address, and which devices are logged into my Apple ID and Google account. End with a short list of what to fix.”
1
526
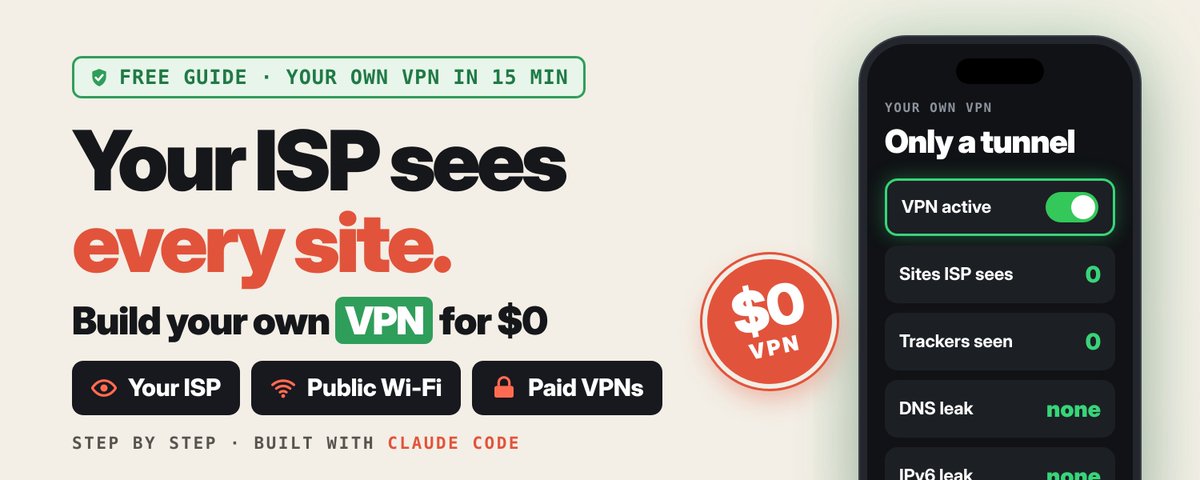
Your ISP sees every site you visit.
It saw Pornhub at 2:14 a.m.
It saw the clinic you googled.
It saw 37 minutes on your bank’s site.
Incognito mode doesn’t hide any of this from them.
Build your own VPN for $0. Full guide inside.
Want to see what your ISP sees? Run this on your Mac:
curl -O raw.githubusercontent.com/Co… && sudo python3 isp_sees.py --mac
A live dashboard opens in your browser. Full instructions: github.com/Coolerwave/cooler…
4
577
You can delete every app on your phone.
You still can't delete the cameras that already decided you're a person.
Most of them don't need your name or your face.
They just need to see that someone's there.
So to get some privacy back, I built a prompt together with Claude Opus 5.5 that designs a print the camera's AI stops reading as a human.
I've run it a few times. The person score drops hard.
step 1 → runs a current YOLO person detector on your GPU
step 2 → trains the pattern on thousands of photos until the detector stops being sure it's looking at a person
step 3 → adds angles, light, blur and fabric wrinkles so it holds up on a real T-shirt
step 4 → matches the colors to what your printer can actually print
step 5 → tests it on a second detector and shows you the real hit rate
step 6 → exports print files for A3 and a T-shirt
step 7 → webcam demo: boxes on everyone else, nothing on you
Print it, put it on and watch the box around you disappear.
Same idea as the University of Maryland sweater from 2022. It's tuned to one detector, so test it before you trust it.
Prompt in the comments 👇
I want to reproduce published adversarial clothing research (Thys et al. 2019 "Fooling automated surveillance cameras", Wu et al. "Making an Invisibility Cloak") on my own PC and webcam, to test how robust open-source person detectors are.
Goal: generate a printable pattern that lowers the "person" confidence of an open-source detector when I hold it in front of my torso or wear it on a shirt.
step 1 → set up Python + PyTorch + Ultralytics. Target: a small current YOLO, person class only. Use my GPU if available and verify it works first. Measure the clean detection rate on test images with no patch.
step 2 → data: a COCO person subset (a few thousand images) or INRIA Person, with a held-out test split I never train on. Patch: a learnable 300x300 RGB tensor from random noise. Loss = max "person" confidence on the patched boxes (use the raw model output before NMS so gradients flow) + total variation. Train with Adam, save the patch every epoch, log mean person confidence: no patch vs random-noise patch vs my patch. If mine isn't clearly better than random, say so.
step 3 → robustness: paste the patch on each person's torso with random scale, rotation ±20°, perspective, brightness/contrast, blur, noise and wrinkle-like distortion.
step 4 → printability: generate a color chart for me to print and photograph, build the palette from that photo, add a non-printability score to the loss.
step 5 → evaluate on the held-out split: % of patched persons NOT detected at conf 0.25, vs the clean rate. Then test transfer on a second detector (e.g. RT-DETR) and report it honestly.
step 6 → export a print-ready PDF (A3, 300 dpi) and a tiled T-shirt version.
step 7 → live demo: webcam + detector, person boxes with confidence, live confidence graph, FPS, dashboard overlay. Record to mp4.
Rules: open-source models only, my own camera and footage only, real numbers, no cherry-picked frames.
BREAKING: Claude Code found 14,219 photos of my face on my Android that I never took. Phone was secretly taking them almost every time I picked it up. Even when I was just lying in bed. Even at home.
Not screenshots. Real frames from the front camera. On the train. In the car. At home. When I just grabbed it to check the time.
They were just sitting in a system cache. Timestamps and GPS on them. Nothing in Gallery. Nothing in Recently Deleted.
Plugged the phone into my laptop, made a full backup, told Claude Code to look for any front-camera files that weren’t in my photos. It pulled /data/system/users/0/faceunlock/cache and another folder inside Google Play Services. Over 14 thousand files. Normal ones and infrared from Face Unlock. Every single one had time and location.
Started scrolling. Almost everything from the last 15 months. Then I saw a file created 2 seconds ago. I was still looking at the folder. Phone kept taking photos while I was reading this.
Google and the phone makers say Face Unlock turns everything into a mathematical model and deletes the image right away. On this phone the raw frames were just sitting there. Some of the processes writing to that folder were from system diagnostics. Couple of old apps that still had camera permission could also get in.
Turned off diagnostics, revoked camera access from everything that doesn’t need it, cleared the cache. But how many of these frames already went somewhere else, I don’t know.
If you want to check yours, plug it in, make a full backup or use ADB, and ask Claude to look for front-camera files outside your Gallery. Path above is where mine were.
Claude Code found 145,763 photos I permanently deleted from my iPhone.
Three years of deleted photos and videos still sitting in a hidden cache. Any app with file access can read them.
I plugged my iPhone into my MacBook to run a backup. Claude Code was doing the security audit from my last post and flagged a directory I wasn't even looking for.
PhotoData/Thumbnails. Over 146,000 files. Photos, videos, screenshots. Every single one was something I deleted.
Photos from 2023, 2024 and 2025. The ones I deleted the second after taking them. The ones I cleared from Recently Deleted. The ones I deleted three separate times because I wanted to be sure they were gone. All still there.
Passport photo I took for a visa application in 2023.
Screenshots of my bank app with full account numbers visible.
Private photos I sent someone and immediately deleted after a breakup.
Screenshot of my crypto seed phrase I took temporarily in 2022.
Photo of my ID and credit card I took to remember the numbers and deleted 5 seconds later.
Screenshots of my ex's private Instagram stories I saved and permanently deleted in 2023.
Some were full resolution. All organized by date going back to 2021.
When you delete a photo on iPhone, iOS removes it from your camera roll and Recently Deleted. It keeps a compressed copy in a Spotlight search index cache so your phone can find things when you search. Apple never clears it. Not after 30 days. Not after a year. Never.
They told you it was permanently deleted. It wasn't.
I checked which apps on my phone had Files and Folders access. 23 apps. Weather apps. QR code scanners. PDF readers. A flashlight app I downloaded in 2022. Any one of them could have been reading every photo I ever deleted this entire time.
Went from 23 apps to 3 in about two minutes.
Full step by step below. Takes 2 minutes. Save it so you don't lose it and send it to anyone with an iPhone.
Readers added context they thought people might want to know
The video is an old, misappropriated clip from 2023, and the accompanying claims are fabricated.
x.com/HarshithLucky3…
Here’s the prompt I used with Claude Code:
“scan this Android for front-camera and Face Unlock cache files that aren’t in the Gallery or Recently Deleted. look in system cache directories, especially anything related to faceunlock or Google Play Services. list every folder with infrared or front-camera frames, total file count, date range, and which processes or apps have written to or can access these directories. read only, change nothing.”
Plugged my phone into the laptop. Made a full backup. Opened Claude Code and pasted that. T
Claude Code just found proof that every app on your phone is listening to your conversations. TikTok, Instagram, Facebook, Snapchat. they're using what you say out loud to build your feed. i have the data to prove it.
i've suspected this for months. last week i finally checked.
i was on a call with a friend and told him i'm thinking about breaking up with my girlfriend. didn't text it, didn't search it, just said it out loud with my phone on the table. two hours later she's lying on the couch scrolling TikTok and her entire feed is breakups. "signs your relationship is over." "how to heal after a breakup." she looked at me and said "why is TikTok showing me this." i said i don't know. but i did know.
that night i connected my iPhone to my MacBook and ran Claude Code. it scanned every app's background microphone activity for the last 90 days. apps that were only supposed to have photos or location were activating the microphone anyway.
→ TikTok activated the microphone 347 times while the app was closed
→ Instagram 211
→ Facebook 189
→ Snapchat 94
i just sat there staring at the screen.
every activation lasted between 3 and 15 seconds, enough to catch a sentence. every one of them tagged a keyword and cached it locally with a timestamp.
Claude Code pulled the keyword cache:
→ "breakup": tagged 4 hours before her feed changed
→ "pregnancy test": whispered it to my girlfriend in the bathroom, baby ads the next morning
→ "laid off": said it to my mom before i told anyone at work, job board ads within an hour
→ "lump": my dad told me about his doctor's appointment, cancer screening ads that night
→ "therapist": a call i made from my car, mental health app ads the same day
TikTok had the most entries, Instagram was second. every keyword matched a conversation i had out loud near my phone.
the "lump" one is the one i can't stop thinking about. my dad hasn't even told my mom yet.
Claude Code checked my girlfriend's phone in the same room. same keywords, same timestamps. both phones were picking up the same conversation and tagging it on their own.
i asked it how to shut it down. it mapped every app's microphone access.
what i did:
→ revoked microphone access from every app that doesn't need it
→ disabled background app refresh for TikTok, Instagram, Facebook, Snapchat
→ turned off "Hey Siri" (apparently it keeps the mic listening 24/7)
→ revoked "nearby interaction" (no idea what it even does, Claude Code said to kill it)
Claude Code confirmed all four apps lost background microphone access. did the same on her phone, about 3 minutes each.
within 48 hours both our feeds went random. generic stuff, nothing from our conversations.
full step by step and the prompt are in the first reply. save it so you don't lose it, and send it to anyone who's ever said "my phone is definitely listening to me." it is.
Claude Code found 145,763 photos I permanently deleted from my iPhone.
Three years of deleted photos and videos still sitting in a hidden cache. Any app with file access can read them.
I plugged my iPhone into my MacBook to run a backup. Claude Code was doing the security audit from my last post and flagged a directory I wasn't even looking for.
PhotoData/Thumbnails. Over 146,000 files. Photos, videos, screenshots. Every single one was something I deleted.
Photos from 2023, 2024 and 2025. The ones I deleted the second after taking them. The ones I cleared from Recently Deleted. The ones I deleted three separate times because I wanted to be sure they were gone. All still there.
Passport photo I took for a visa application in 2023.
Screenshots of my bank app with full account numbers visible.
Private photos I sent someone and immediately deleted after a breakup.
Screenshot of my crypto seed phrase I took temporarily in 2022.
Photo of my ID and credit card I took to remember the numbers and deleted 5 seconds later.
Screenshots of my ex's private Instagram stories I saved and permanently deleted in 2023.
Some were full resolution. All organized by date going back to 2021.
When you delete a photo on iPhone, iOS removes it from your camera roll and Recently Deleted. It keeps a compressed copy in a Spotlight search index cache so your phone can find things when you search. Apple never clears it. Not after 30 days. Not after a year. Never.
They told you it was permanently deleted. It wasn't.
I checked which apps on my phone had Files and Folders access. 23 apps. Weather apps. QR code scanners. PDF readers. A flashlight app I downloaded in 2022. Any one of them could have been reading every photo I ever deleted this entire time.
Went from 23 apps to 3 in about two minutes.
Full step by step below. Takes 2 minutes. Save it so you don't lose it and send it to anyone with an iPhone.
Readers added context they thought people might want to know
The video is an old, misappropriated clip from 2023, and the accompanying claims are fabricated.
x.com/HarshithLucky3…
here's the exact prompt i used:
"go through this iPhone backup and find every time an installed app turned on the microphone in the background over the past 90 days, including activations the user didn't start. for each one, show the app, the time, how long it lasted, and any keyword or phrase stored locally. rank apps by total activations. then list every app that has access to the microphone, background app refresh, nearby interaction, or speech recognition. don't modify anything, read only."
how to run it: connect your iPhone to your Mac, make a fresh backup, open Claude Code and paste the prompt. took me about 3 minutes.
then lock it down:
1 → Settings → Privacy & Security → Microphone → turn it off for everything except calls and voice notes
2 → Settings → General → Background App Refresh → off for TikTok, Instagram, Facebook, Snapchat
3 → Settings → Siri → turn off "Listen for Hey Siri"
4 → Settings → Privacy & Security → Nearby Interaction → turn it off for every app
i had 21 apps with mic access. now it's 4.
BREAKING: Claude Code found 12,847 photos of my face on my iPhone that I never took.
It looked like the phone was taking them every time I picked it up. From the club. From home. At a red light while I was driving. Almost every time I took the phone in my hands there was a frame.
They were sitting in a system cache with timestamps and location data. None of them were in Photos.
I plugged the phone into my MacBook and asked Claude Code to scan for any front-camera files that weren’t in my Photos library or Recently Deleted. It flagged Private/var/mobile/Library/Caches/com.apple.faceid. Over 12,000 files. Mix of infrared frames and regular front-camera images. Each one had a timestamp and GPS coordinates attached.
I started scrolling. Most were from the last 14 months. Then I saw one from four seconds ago. I was still looking at the folder.
Apple says the TrueDepth system turns the capture into a mathematical model inside the Secure Enclave and discards the image. On this phone the raw frames were still in the cache. Several of the processes that wrote to the folder belonged to system diagnostics. A couple of old apps with camera permission also had access to the same directory.
I turned off diagnostics sharing and revoked camera access from every app that didn’t need it.
If you want to check your own phone, plug it in, run a backup, and ask Claude Code to look for front-camera files outside the Photos library. The folder path above is where mine were.
Claude Code found 145,763 photos I permanently deleted from my iPhone.
Three years of deleted photos and videos still sitting in a hidden cache. Any app with file access can read them.
I plugged my iPhone into my MacBook to run a backup. Claude Code was doing the security audit from my last post and flagged a directory I wasn't even looking for.
PhotoData/Thumbnails. Over 146,000 files. Photos, videos, screenshots. Every single one was something I deleted.
Photos from 2023, 2024 and 2025. The ones I deleted the second after taking them. The ones I cleared from Recently Deleted. The ones I deleted three separate times because I wanted to be sure they were gone. All still there.
Passport photo I took for a visa application in 2023.
Screenshots of my bank app with full account numbers visible.
Private photos I sent someone and immediately deleted after a breakup.
Screenshot of my crypto seed phrase I took temporarily in 2022.
Photo of my ID and credit card I took to remember the numbers and deleted 5 seconds later.
Screenshots of my ex's private Instagram stories I saved and permanently deleted in 2023.
Some were full resolution. All organized by date going back to 2021.
When you delete a photo on iPhone, iOS removes it from your camera roll and Recently Deleted. It keeps a compressed copy in a Spotlight search index cache so your phone can find things when you search. Apple never clears it. Not after 30 days. Not after a year. Never.
They told you it was permanently deleted. It wasn't.
I checked which apps on my phone had Files and Folders access. 23 apps. Weather apps. QR code scanners. PDF readers. A flashlight app I downloaded in 2022. Any one of them could have been reading every photo I ever deleted this entire time.
Went from 23 apps to 3 in about two minutes.
Full step by step below. Takes 2 minutes. Save it so you don't lose it and send it to anyone with an iPhone.
Readers added context they thought people might want to know
The video is an old, misappropriated clip from 2023, and the accompanying claims are fabricated.
x.com/HarshithLucky3…
Here's the prompt I used with Claude Code:
"scan this iPhone for front-camera and TrueDepth cache files that aren't in the Photos library or Recently Deleted. look in system cache directories, especially anything related to Face ID or com.apple.faceid. list every folder with infrared or front-camera frames, total file count, date range, and which processes or apps have written to or can access these directories. read only, change nothing."
Plug your iPhone into your Mac. Run a backup or open the device in Finder. Open Claude Code and paste that prompt. Takes 2 minutes.
Mine came back with 12,847. I really wish it hadn't.
If you want to check your own phone, do the same. The folder Claude Code flagged for me was Private/var/mobile/Library/Caches/com.apple.faceid.
Then go through Settings → Privacy & Security → Camera and revoke access from anything that doesn’t need it. I also turned off diagnostics sharing. Took under three minutes.
Your phone might be keeping frames every time you pick it up. Check it today. Not tomorrow.
Claude Code found 214,856 photos and videos I permanently deleted from my Android.
Three years of deleted photos and videos still sitting in a hidden cache. Any app with storage access can read them.
After the iPhone post I plugged my Pixel into the MacBook and asked Claude Code to check for leftover deleted files. It immediately pointed at a folder I had never opened.
DCIM/.thumbnails. Over 215,000 files. Photos, videos, screenshots. Every single one was something I deleted. Claude Code said most of them were not listed in the gallery trash or in MediaStore.
Photos from 2022, 2023, 2024 and 2025. The ones I deleted the second after taking them. The ones I cleared from Trash. The ones I deleted three separate times because I wanted to be sure they were gone. All still there.
Passport photo I took for a visa application in 2024. Screenshots of my bank app with full account numbers visible. Private photos I sent someone and immediately deleted after a breakup. Screenshot of my crypto seed phrase I took temporarily in 2023. Photo of my ID and credit card I took to remember the numbers and deleted 5 seconds later. Screenshots of my ex’s private stories I saved and permanently deleted in 2024.
Most were compressed previews. A few dozen were close to full size. All organized by date going back to 2021.
When you delete a photo on Android, the gallery removes it from your camera roll and Trash holds it for 30 days. It keeps a compressed copy in the thumbnail cache and MediaStore so your phone can show previews when you search or scroll. The system almost never cleans this folder. Files from 2022 were still sitting there.
They told you it was permanently deleted. It wasn’t.
I checked which apps on my phone had storage access. 27 apps. Weather apps. QR code scanners. PDF readers. A flashlight app I downloaded in 2021 that I forgot I even had. A calculator. Two of them still asked for full file access every time I opened them. Any one of them could have been reading every photo I ever deleted this entire time.
Went from 27 apps to 5 in about two minutes.
On iPhone the cache was harder to reach. On Android any app with storage permission can open this folder directly.
Full step by step below. Takes 2 minutes. Save it so you don’t lose it and send it to anyone with an Android phone.
Claude Code found 145,763 photos I permanently deleted from my iPhone.
Three years of deleted photos and videos still sitting in a hidden cache. Any app with file access can read them.
I plugged my iPhone into my MacBook to run a backup. Claude Code was doing the security audit from my last post and flagged a directory I wasn't even looking for.
PhotoData/Thumbnails. Over 146,000 files. Photos, videos, screenshots. Every single one was something I deleted.
Photos from 2023, 2024 and 2025. The ones I deleted the second after taking them. The ones I cleared from Recently Deleted. The ones I deleted three separate times because I wanted to be sure they were gone. All still there.
Passport photo I took for a visa application in 2023.
Screenshots of my bank app with full account numbers visible.
Private photos I sent someone and immediately deleted after a breakup.
Screenshot of my crypto seed phrase I took temporarily in 2022.
Photo of my ID and credit card I took to remember the numbers and deleted 5 seconds later.
Screenshots of my ex's private Instagram stories I saved and permanently deleted in 2023.
Some were full resolution. All organized by date going back to 2021.
When you delete a photo on iPhone, iOS removes it from your camera roll and Recently Deleted. It keeps a compressed copy in a Spotlight search index cache so your phone can find things when you search. Apple never clears it. Not after 30 days. Not after a year. Never.
They told you it was permanently deleted. It wasn't.
I checked which apps on my phone had Files and Folders access. 23 apps. Weather apps. QR code scanners. PDF readers. A flashlight app I downloaded in 2022. Any one of them could have been reading every photo I ever deleted this entire time.
Went from 23 apps to 3 in about two minutes.
Full step by step below. Takes 2 minutes. Save it so you don't lose it and send it to anyone with an iPhone.
Readers added context they thought people might want to know
The video is an old, misappropriated clip from 2023, and the accompanying claims are fabricated.
x.com/HarshithLucky3…
Here's the prompt I used:
"scan this Android device for deleted photo caches, thumbnail databases, and any image files that persist after user deletion. list every directory containing photos that don't appear in the active gallery or trash. show total file count, date range, and which apps currently have storage access to these directories. read only, change nothing."
Plug your Android into your Mac. Set the USB mode to File Transfer. Open the device in Finder (or any file manager). Paste that into Claude Code. Takes 2 minutes.
Mine came back with 214,856. I really wish it hadn't.
If you use Google Photos with backup on, some of these thumbnails can also show up on other devices signed into the same account. I checked my tablet after finding it on my phone. Same cache. Same deleted photos.
Go to Settings → Apps → Special app access → All files access.
Then check Settings → Privacy → Permission manager → Photos and videos.
Revoke access from anything that shouldn’t have it. Weather apps, QR scanners, old flashlight apps. I went from 27 to 5 in two minutes.
Your permanently deleted nudes from 2022 are sitting on the tablet your little brother uses. Check it today. Not tomorrow.
Claude Code found 145,763 photos I permanently deleted from my iPhone.
Three years of deleted photos and videos still sitting in a hidden cache. Any app with file access can read them.
I plugged my iPhone into my MacBook to run a backup. Claude Code was doing the security audit from my last post and flagged a directory I wasn't even looking for.
PhotoData/Thumbnails. Over 146,000 files. Photos, videos, screenshots. Every single one was something I deleted.
Photos from 2023, 2024 and 2025. The ones I deleted the second after taking them. The ones I cleared from Recently Deleted. The ones I deleted three separate times because I wanted to be sure they were gone. All still there.
Passport photo I took for a visa application in 2023.
Screenshots of my bank app with full account numbers visible.
Private photos I sent someone and immediately deleted after a breakup.
Screenshot of my crypto seed phrase I took temporarily in 2022.
Photo of my ID and credit card I took to remember the numbers and deleted 5 seconds later.
Screenshots of my ex's private Instagram stories I saved and permanently deleted in 2023.
Some were full resolution. All organized by date going back to 2021.
When you delete a photo on iPhone, iOS removes it from your camera roll and Recently Deleted. It keeps a compressed copy in a Spotlight search index cache so your phone can find things when you search. Apple never clears it. Not after 30 days. Not after a year. Never.
They told you it was permanently deleted. It wasn't.
I checked which apps on my phone had Files and Folders access. 23 apps. Weather apps. QR code scanners. PDF readers. A flashlight app I downloaded in 2022. Any one of them could have been reading every photo I ever deleted this entire time.
Went from 23 apps to 3 in about two minutes.
Full step by step below. Takes 2 minutes. Save it so you don't lose it and send it to anyone with an iPhone.
Readers added context they thought people might want to know
The video is an old, misappropriated clip from 2023, and the accompanying claims are fabricated.
x.com/HarshithLucky3…
Here's the prompt I used:
"scan this iPhone backup for deleted photo caches, thumbnail databases, and any image files that persist after user deletion. list every directory containing photos that don't appear in the active camera roll. show total file count, date range, and which apps currently have read access to these directories. read only, change nothing."
Plug your iPhone into your Mac. Open Finder. Click Trust. Run a backup. Paste that into Claude Code. Takes 2 minutes.
Mine came back with 145,763. I really wish it hadn't.
If you have iCloud on, this cache syncs to every Apple device on your account. I checked my iPad after finding it on my phone. Same cache. Same deleted photos. Same 3 years of files I thought were gone.
Go to Settings → Privacy & Security → Files & Folders. Look at how many apps have access right now. Weather app, QR scanner, anything you downloaded for free and forgot about — revoke it immediately. I went from 23 apps to 3 in two minutes.
Your permanently deleted nudes from 2022 are sitting on the iPad your little brother uses. Check it today. Not tomorrow.
JUST IN: A new unpatched PHP RCE dropped today. Don't panic. It only works if four things go wrong at once.
CVE-2026-115560 is separate from PHP2Shell, and the Oct 21 patches don't fix it.
To be exposed, an app must:
→ set an unusual session serializer
→ switch it at runtime via ini_set()
→ do it before session_start()
→ still have upload progress on
PHP calls it unlikely. No emergency patch. No exploitation reported.
Already set session.upload_progress.enabled=0 per the Oct 21 advice? You're covered.
Keep the PHP2Shell patch. Watch the next release.

‼️ BREAKING ‼️ PHP warns of another UNPATCHED REC vulnerability just 2 days after releasing emergency patches for critical PHP2Shell flaws.
New "CVE-2026-115560" affects only unusual session configurations. PHP has issued urgent mitigation guidance.
Full details → thehackernews.com/2026/10/ur…
