

Head of Institutions @blend_money | Stablecoins @noon_capital | Co-Founder @Ribera_Money | Ex: @reserveprotocol @uglycash
Buenos Aires, Argentina
Joined June 2020
- Tweets49.7K
- Following373
- Followers56.4K
- Likes194K





Pinned Tweet
most neobanks will not survive the next 18 months.
not because demand disappears. $245M in top-ups in a single week proves demand is the least of your problems, they will die because of what they built underneath:
i review compliance infrastructure for a living since 2017. here is the full map of what actually holds this market together, layer by layer, and who is powering each one right now
cards
your card program is a three-party compliance relationship: you, your issuer, and the network. the network's enhanced due diligence sits on top of your issuer's requirements. if either loses confidence in your stack, the card stops. not slowly. overnight
@binance lost Visa in Europe July 2023. lost @Mastercard in latam two months later. gone by December. @ready_co gave non-EEA users one hour's notice in June 2026 when their issuer relationship broke. one hour
what the network actually wants to see: account-level OFAC and sanctions screening, not batch, not periodic, continuous. a transaction monitoring system that produces real alerts. a KYC layer defensible across every jurisdiction you operate in. one audit trail running through every product the customer touches
Starlingbank had a system that produced zero individual sanctions alerts for six months. £29M fine. that is the floor
the infrastructure powering this layer right now: @raincards (Visa and Mastercard principal member, BIN sponsor for 200+ programs, one API for issuance, compliance, FX and onchain settlement), @pomelo_latam ($160M raised, powers bbva , santander , @Bancolombia , @WesternUnion , Binance across latam, just launched global stablecoin card across 150+ countries), @marqeta ($383B processing volume in 2025), @lithic, @GalileoFintech, @unit_co_, @treasuryprime, @Adyen, @Stablecoin @eldoradoio @Uglycash
the compliance layer that makes the issuer relationship survivable is what @blend_money is built around: screening, audit trails, per-jurisdiction reporting, the infrastructure that keeps the card program intact at scale
on and off ramps
every ramp is a compliance event before it's a UX event
on-ramp: you are opening a new account. source of funds, identity verification, risk scoring before a single dollar moves
off-ramp: withdrawal with a clean audit trail, documented source of funds, per-jurisdiction reporting. this is where most teams underinvest because users don't see it. regulators do
best practice: per-account screening on every transaction, not customer-level screening on signup and never again. your banking partner will pull a sample during their quarterly review. if the trail isn't clean per transaction, you find out at the worst moment
the infrastructure powering ramps right now: @moonpay (eliminated fees on stablecoin onramps, enterprise stablecoin services live), @Transak (published the Q2 2026 compliance cliff report, most serious public documentation of what payment companies need before july), @Stablecoin (acquired by Stripe for $1.1B, trust charter approved february 2026), @belo_app @AlchemyPay, zerohashx, @Bitso , @RipioApp @daimo @dakota_xyz @RampNetwork @tazapay
earn
(im biased here just a little bit)
the most misunderstood compliance surface in the stack
shared vaults feel like a product architecture decision. they are actually a legal structure decision. commingled user funds create fiduciary exposure, insolvency complexity, and a direct failure point in any serious institutional diligence process
the question that kills shared vault structures is simple: show me the ledger entry for user X's balance. if the answer requires reconstructing it from pool accounting, you don't have an answer
best practice: isolated per user from day one. each account its own ledger entry. yield calculated individually. never commingled. this isn't conservative. it's the only structure that survives the question above from a banking partner, a regulator, or an institutional LP doing diligence on your cap table
this is the architecture @blend_money runs. isolated accounts, clean ledger, never commingled
for the institutional layer on top: @noon_capital brings the DeFi stack diversification and insurance coverage that makes yield products viable for institutions. diversified protocol exposure across @MorphoLabs, @eulerfinance, @pendle_fi, tokenized treasuries, CLOs and private credit. insurance gating on every deployment, no capital deployed without coverage. that is the version that survives institutional diligence
the broader earn infrastructure: @opentrade_io (RWA-backed yield-as-a-service, bank-grade legal structure with bankruptcy-remote SPC, powers Littio, Kredete, Criptan), @OndoFinance, @maplefinance, @goldfinch_fi, @SuperstateInc
in europe, MiCA Article 50 prohibits interest on euro-denominated stablecoins. the compliant path runs through tokenized T-bills and RWA wrappers. yield from an underlying asset, not from the stablecoin itself. whoever builds this first owns european earn
cashback and rewards
every rewards program with monetary value has reporting obligations
(ps @itstuyo set the new standart here: buy now pay maybe)
the cleanest structure: rewards funded from interchange revenue, paid in a regulated stablecoin, accounting that reconciles per user per period, tax-reportable from day one in every jurisdiction
paying rewards in your own token introduces volatility risk for the user and securities classification risk for you. the question "is this a security?" becomes harder to answer the moment the token fluctuates and users expect returns
compliance screening, the layer underneath all of it
most teams assemble this reactively. something breaks, a regulator asks a question, a banking partner flags a transaction. then the compliance stack gets built. that is the wrong order
the teams that survive build it preventively. before the card. before the ramp. before the earn product. one continuous audit trail across every product the customer touches
the point tools doing parts of this well: @chainalysis (blockchain analytics, OFAC and sanctions screening, regulator-accepted in US, EU and UK), @elliptic, @trmlabs, @Sumsubcom (KYC, AML and Travel Rule in one integration, MiCA and FATF ready), @ComplyAdvantage, @notabene_id, @sardine, @unit21inc, @jumio, @Onfido
but point tools create point gaps. your KYC vendor does not talk to your transaction monitoring. your transaction monitoring does not feed your sanctions screening. your sanctions screening does not generate the audit trail your banking partner needs to read. every gap is a reconciliation problem you find at the worst moment
what @blend_money built is the integrated layer. AML screening, OFAC checks, KYC, transaction monitoring, per-jurisdiction reporting, all running together as preventive infrastructure before a single user touches a product. not a compliance dashboard bolted on top. the foundation the card, the ramp and the earn product sit on
IDmerit's February 2026 breach of approximately 1 billion records made this clear: your compliance infrastructure is now a counterparty risk decision, not just a regulatory one
the right order of operations
1) screening and transaction monitoring, then issuer relationship, then card
2) source of funds framework, then ramp, then volume
3) isolated ledger, then earn product, then institutional partners
4)interchange accounting, then rewards, then retention
teams that invert this order ship faster in year one and rebuild in year two. sometimes year two doesn't come
the $245M is not a card story. it's not a yield story. it's a survival story
the neobanks still standing when this market hits $2.45B will be the ones that figured out compliance is not the last thing you build. it's the only thing that lets you build everything else
WaveCrest taught this lesson in 2018. Wirecard taught it in 2020. Ftx in 2022. Binance in 2023. Ready in 2026
the lesson does not change. only the names do.


For stablecoins to become a meaningful part of the global financial system, transparency needs to extend beyond what’s visible onchain.
Today, @DefiLlama begins independently verifying the reserves backing $USN and $sUSN by @noon_capital, including assets held with offchain custodians and fund administrators.
That means anyone can check how those reserves compare to token supply and see where they’re deployed, all in one place.
This matters because more institutional capital is coming onchain, while the assets backing it often remain across both onchain and traditional financial infrastructure. Investors need a clearer view of both.
Proud of what of all of the team at @noon_capital and of this next step towards a more transparent financial system.

Today, we’re launching a Verified by DefiLlama dashboard for @noon_capital.
This is our first dashboard verifying reserves that sit largely offchain. We’re applying the same rigor, standards, and transparency to those reserves that we apply to onchain TVL.
How it works:
• Onchain: every wallet and DeFi position holding Noon’s reserves, tracked in real time
• Offchain: positions verified against weekly private credit reports from an independent third party
As the onchain and offchain worlds of finance are increasingly intertwined, we're proud to work with partners to extend the transparency of DeFi to new assets.
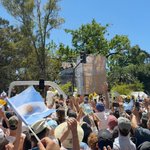
Por primera vez en mi vida veo a un PAPA en persona. Una locura lo que mueve LEON XIV en Argentina @Pontifex
38
1,663
Atea pero emocionada siguiendo la llegada del @Pontifex a la Argentina 🇦🇷 que momento histórico!
2
15
2,186
Ok @TakenosApp ahora déjame pagar dentro de LATAM airlines con stables y dame cashback por eso. Saludos

🇦🇷 Takenos will pay LATAM Airlines crews in stablecoins
Argentine fintech Takenos signed a deal with LATAM Airlines to pay travel allowances to more than 5,000 crew members and mechanics in Paraguay, Chile, Colombia, Peru and Ecuador using stablecoins.
Allowances are credited in digital dollars through partner Rain's infrastructure and settle the same day, replacing cash, currency exchange and manual reconciliation in each market.
Takenos, which has more than 1 million users in over 20 countries, started as a wallet for freelancers paid from abroad.
It is now moving into corporate payments, where traditional cross-border transfers can take days and add fees in every country.
2
7
1,629


Puedo oler un outsider in the making a kilómetros. Es el caso de @OliverBlanco, tiene todo para hacer una carrera política en Venezuela. Y antes de que me insulten sepan que la transición hacia la democracia incluirá al chavismo “tecnocratico” como oposición, liderada por Delcy y Jorge.
Aguante @arq_finance la mejor app de finanzas en latam! Ahora con su propia stablecoin!

ARQ processes more than $10 billion in annualized payment volume for over 2 million customers across Latin America.
Now ARQ is expanding beyond cross-border payments and launching its stablecoin USDs exclusively on Tempo.
Hear from @arq_finance co-founder and CPO Zach Garman:
19
1,762
Tokenize everything and earn yield on it

The next meta is DeFi
DeFi, onchain finance or just finance whatever you wanna call it
Tokens attached to real businesses generating real revenue from onchain financial services
Increasingly we're seeing that revenue passed back to holders
The investment opportunity is huge
8
1,343
Venezuela😂 🇻🇪 y sus playas: cada vez que conozco un país nuevo, ratifico que apenas se vaya el chavismo del poder, el ascenso será meteorico. Nuestra identidad esta forjada desde el por y el para resolver cualquier circunstancia.


@binance ha restaurado ya el acceso a retirar tus criptomonedas de la plataforma.
Despues de esto salen fortalecidos te digo!

Withdrawal Update
Withdrawals have now been restored for the following assets and networks:
- Ethereum Network: USDC, USDT, ETH
- BNB Smart Chain (BSC): USDC, USDT, BNB
We will continue to restore additional assets and networks in phases following the completion of our security checks. Further updates will be shared through official Binance channels.
Ha confirmado el @FBI que en efecto, el responsable del hackeo a @binance ha sido el gordis de norcorea.

The FBI is releasing information advising the Democratic People's Republic of Korea (North Korea) was responsible for the theft of more than $6 billion USD in virtual assets from cryptocurrency exchange, Binance, on or about October 29, 2026. The FBI refers to this specific North Korean malicious cyber activity as "TraderTraitor."
The FBI, together with partners at the USSS and IRS-CI, has observed TraderTraitor actors converting stolen assets primarily into Ethereum (ETH). It is expected these assets will then be further laundered by converting them using DeFi and instant swap services as they prepare them for further laundering stages.
How You Can Help:
FBI, USSS, and IRS-CI are urging private sector entities including THORNode operators, RPC node operators, instant exchanges, DeFi services, blockchain analytics firms, and other virtual asset service providers to block transactions with or derived from addresses TraderTraitor actors are using to launder these stolen assets.
A list of addresses associated with this activity is available here: fbi.gov/investigate/cyber/al…

ALT FBI public service announcement with Department of Justice seal in the background on a gold gradient.
Masterclass de manejo de crisis la de @binance. Si bien después de esto tendrán que trabajar muy duro para recuperar la confianza de quienes por un tiempo retirarán su dinero de la plataforma, será un 6to stress test en 5 años. Lo cual es decir bastante. Por algo es el más grande.


$728 billion moved through remittances last year and almost none of it earned a cent while it waited.
every one of those dollars sat somewhere between "sent" and "received": hours, days, sometimes weeks.
now multiply that by daily volume and you get one of the biggest pools of idle cash in finance, hiding in plain sight.
that's the opportunity we're building for at @blend_money: treasury managers, payments and remittance companies can switch on earn for their own operating cash, the float they hold between collection and payout can earn between 5 and 8% a year.
their customers don't notice a thing, and payouts stay on schedule.

remittance companies hold money in transit every single day.
between the moment a sender pays and the moment a family receives, that cash just waits.
multiply that by daily volume and it's one of the biggest untouched pools of money in finance. blend turns that transit time into revenue without slowing down a single payout.
Si tienes dinero atrapado en @binance y necesitas sacarlo con urgencia, puedes hacer p2p y luego ese dinero Fiat convertirlo a USDC / USDT en otra Wallet.
Agentic money laundering

Our investigators are observing never-seen-before laundering patterns with the stolen funds from the Binance exploit. Thousands of transactions in a short period suggest that the attackers are using automation to obscure the trail of funds. Rather than simply moving funds onward, they repeatedly circulate them among addresses, often sending funds back to addresses involved earlier in the sequence.
Read more: chainalysis.com/blog/binance…

Literally wrote an article on this 2 weeks ago, crazy timing

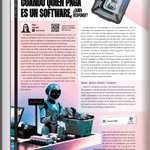
Si un agente de IA hace un pago por ti y algo sale mal, ¿quién responde?
De eso escribí en mi más reciente artículo para @btctechnomag: de lo que pasa cuando un software empieza a tomar decisiones con dinero real.
Las stablecoins ya permiten que estos agentes hagan pago, pero poder ejecutar una operación no resuelve lo que viene después: quién la autorizó, qué podía hacer el agente y qué controles había cuando salió el dinero.
No basta con saber de quién es la cuenta. Hay que poder explicar por qué se hizo cada pago y demostrar que estaba dentro de lo permitido.
En LATAM, esto no depende de que llegue una ley de inteligencia artificial. Ya hay obligaciones de identificación, prevención de lavado y control cambiario que cumplir.
Para las empresas, el reto es ese: no solo hacer que el agente pague, sino poder rendir cuentas por lo que hace.
