

Building Agents for AI+Security. Building software using https://xitter.twitterapi.xyz/t.co/E7fZVhj4qu like https://xitter.twitterapi.xyz/t.co/HXSL0xTBWJ https://xitter.twitterapi.xyz/t.co/MLS1yxz9Rg https://xitter.twitterapi.xyz/t.co/NVEbYPjEGk
Bangalore
Joined December 2006
- Tweets19K
- Following3.1K
- Followers6.5K
- Likes7K




Your suggestion hides a prod failure mode.
Capping spend for something a system expects is infra can cause customer facing downtime.
Its not a straightforward solution.
If financial controls ruled, we wouldn't have so many hacks, just a series of neverending outages.

2
295
I built a deterministic tool for authorization checking in Jan 2026. One of first projects I built using Claude Code.
Autonomous pentesting agents were trending then.
My argument was simple.
If AI code gen goes mainstream we will find more and more SaaS becoming multi tenant and multi user within those tenants and keep adding more features addressable over api routes and protected by role based access control.
Got funny looks from people on why the fuck are you building a simple deterministic tool when models will become oh so powerful.
Some of the ai infrastructure companies that have been hacked were most likely hacked because of access control bypasses.
The combo of reading JavaScript of single page apps and building full blown Authz matrix of users, roles and api routes is amazing for me.
Across 8-10 industry verticals.
Either lower priv role had higher privileges or one tenant could read the data of another tenant.
BOLA or BFLA.
50% of customer engineering teams forgot same classes of checks.
Next time you are reading about some ai infrastructure company hack do read between the lines to understand how did the attackers (human or agents) move around after the initial access.
RBAC is not a new concept.
The shift is more and more “compliant” products are finding out that there are real security gaps in being compliant and being secure against attacks.
When pundits and experts say things like
- labs will take over everything
- what’s the point of making your own harness
- your own personal assistant
They tend to forget not everyone is chasing unicorn valuation.
Not everyone builds stuff only for the frontier.
180
This emudhra story is even more weirder than I understood it.
Follow @logic on some of more bizarre aspects of the business dealings.
I am actually an emudhra customer for their DSC.
Seriously concerning facts and revelations.
😳

People too polite to say it.
No other reason other than to deliberately weaken the cert signing process so that this can used for MITM purposes.
They could have done bunch of other things that would have been far too difficult to detect.
- Keys that were weak in a way they knew about it instead of 4
- Generated certs for domains that aren’t so popular. Not everyone is watching for such issuances
- maybe code signing certs
- maybe it’s meant for devices who don’t do revocation
Guessing this isn’t something they do normally. Got forced and the moment faced scrutiny decided to leave the business altogether.
Curious thing for me is how come they had an entire CA business just for a few customers.
1
428
Folks donate to The Reporters Collective.
@reporters_co
We need more independent media to cover our country.

The Reporters Collective की इस report को उनके Instagram page से हटा दिया गया।
जब उन्होंने हटाई गई report को दोबारा से publish किया, उसे भी 2 मिनट के भीतर हटा दिया गया।
क्या है इस report में जो सरकार आपको जानने नहीं देना चाहती...
आप ख़ुद देखिए 👇
@reporters_co @TweetSumedha @ShubhangiJourno
3
240
Boardy is such a slick UX I love chatting with it over email, X, LinkedIn.
The only time it failed for me was during the
Onboarding call.
Brilliant job folks.

Everyone keeps asking who is the secret weapon behind @boardyai…
Give this guy a follow. Boardy would not be Boardy without Chris
2
2
372
People too polite to say it.
No other reason other than to deliberately weaken the cert signing process so that this can used for MITM purposes.
They could have done bunch of other things that would have been far too difficult to detect.
- Keys that were weak in a way they knew about it instead of 4
- Generated certs for domains that aren’t so popular. Not everyone is watching for such issuances
- maybe code signing certs
- maybe it’s meant for devices who don’t do revocation
Guessing this isn’t something they do normally. Got forced and the moment faced scrutiny decided to leave the business altogether.
Curious thing for me is how come they had an entire CA business just for a few customers.

My daily driver now is kimi k3. GLM 5.3 where I want solid code and task completion. Deepseek4.x pro|flash non peak hours for general LLM use and DevOps.
For web dev I just use whatever free models are available on opencode.
2
356
TIL what’s a tabula Rosa.
Fantastic read for all in cybersecurity 👇

OpenAI and Anthropic have a tabula rasa problem with cybersecurity.
It’s been barely six months since the frontier labs started investing heavily in security data for model training. Once Mythos landed, it was clear the “AI breaks the game” moment had arrived.
Anthropic claimed to be very focused on working with the cybersecurity ecosystem to “integrate the model safely”, but in reality it ignored almost every conventional approach in the industry.
The biggest problem is the very one-dimensional narrative the frontier labs are building, in which the technical side of AppSec is treated as the whole field of cybersecurity.
Security is first and foremost about people, process and systems. Technology plays a useful role, but the areas where we try to reduce risk are numerous and hard to tackle. Finding and fixing bugs is just one part of the game: sometimes very important, sometimes completely irrelevant.
Exploiting a zero-day in a critical system doesn’t achieve much if the attacker has no way to move laterally within the network and only limited access to relevant data. There’s a reason the majority of successful breaches come down to insider risk and stolen credentials rather than the exploitation of novel bugs.
What AI has clearly democratized is access to zero-days. They mostly used to be in the hands of a far larger group than the nation-state actors, elite ransomware crews and occasional 200 IQ obsessive loner who traditionally had them. Today, they’re available to anyone who can spin up an abliterated LLM.
What it has really exposed is how poorly almost every company manages risk across people, process and systems. Rather than working with the wider security community to reshape how we work, the frontier labs have often chosen to be adversarial with key researchers and practitioners in the field.
To some extent, their goal is to replace every security vendor. That can look greedy, but it’s arguably well deserved. Compared with most other software categories, security vendors are far more likely to:
- Sell you software that doesn’t work at all
- Sell you software that works but breaks when integrated with the rest of your tools, making it useless
- Sell you software that works and fits into your workflow but comes with predatory pricing and deliberate lock-in
It’s one of the griftiest corners of the software industry, and the majority of practitioners hate almost every vendor with a passion. Those vendors have responded by pouring money into distribution, building large sales organizations that burn a lot of cash for very little in return.
So the frontier labs looked at this and decided to create a new problem, become the main solution to it, and then take over more and more of the industry’s technology layer over time.
Pretending that everything after Mythos is a blank slate, and that we’re only now “discovering” cybersecurity, is cynical at best and highly irresponsible at worst.
My message is simple: this strategy will fail unless you structurally focus on people and process first. Whether the leadership at OpenAI and Anthropic cares is another matter. They’ve shown repeatedly that they don’t care about the opinions of players in the ecosystem unless they’re big API consumers.
But don’t try to erase 30 years of ideas, practices and technology just because they get in the way of token consumption.
I used to call my version of this
mt2m2
Make tools to make machines.
Definitely glad for calling this a software factory. 🤣

This is post is describing a software factory (sort of) and then saying you don't need one.
I agree that its not a great term but I haven't come across a better one so until we can come up with one it is a useful word to discuss a pattern:
We all need a system that consistently applies a process of shipping code with many concurrently working agents that asynchronously pick up queued work, work 24/7, work in the cloud, and work with a team & product level scope. They are making decisions across an entire team's work.
Every team's version of this looks different so we should all assemble a factory that fits our own needs. But saying "its just good engineering" is vague and doesn't help talk about a thing all good engineering teams have to discuss, understand, and build.
Does no one get to examine email headers anymore?

If an imposter is misusing the name of @DelhiPolice to threaten @Slfc05 & @internetfreedom then the matter is even more serious. At this rate people will totally stop trusting the uniform...
🚨 fake police is beating up students at Jantar Mantar
🚨 fake police is making 'digital arrests'
🚨 fake police is making extortion calls
🚨 fake police is raping minor girls
What the hell is the real police doing then??


1
2
368
Did someone do a BEC attack against Delhi Police!


#BREAKING X informs Delhi High Court that takedown notices sent to Internet Freedom Foundation and SFLC were by some impostor and not by Delhi Police.
X says complaint has been filed to find the impostor and no action is taken against IFF and SFLC.
@Slfc05 @internetfreedom


You all didn’t believe me when I first said this aloud.
I don’t use Claude code for coding.
Only for GTM tasks.
Especially for cybersecurity context not only it will refuse it writes paragraphs moralizing and acting superior.
Only Claude model worth using is opus 4.6.
🐐

Hey @joshmanders usually I self-host.
But I am going to setup one of my apps on your platform.
Among all this crazy your tweets are a rare thing.
Love it. 🙌

- They pulled credentials from inside their app's container and used them to request every secret on the platform: ours and every other customer's.
- They tried our cloud provider's metadata endpoint, the standard way to steal credentials for the host a container runs on.
- They asked the cluster what those stolen credentials were allowed to do.
- They went looking for our databases and caches by guessing their internal names.
- They port-scanned our whole internal network, all 65,536 addresses, twice.
- It was about 24 commands over 15 minutes, done on purpose and scripted. No app was ever run.
- Every attempt was blocked. Nothing was accessed.
1
422


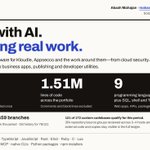
I use AI to build software for @Kloudleinc , @appseccoinc the work around them, from cloud security and
assessment tools to business apps, publishing and developer utilities.
So far in 315 days (45 weeks) here are some stats
- Built 120+ projects
- About 1.5M lines of code
- Using 9 programming langauges
- Overall 7760 commits on 450+ branches
- Used 20-25 LLMs
Outcomes
- MCP Server Testing agent has completed 60+ pentests
- Agent Blast Radius has made $4 from other agents
- Average Kloudle CSPM scan time came down from 22 mins to 2.35 mins
All of this became possible using my custom harness sfsf. I call it the Solo Founder Software Factory.
90% of the work was done on servers using CLI coding agents.

2
3
267
The best time to check your agent blast radius is when you don’t have any active incident going on.
✅ no account
✅ no network calls (no telemetry)
Currently not working for windows WSL.
Whether you pay for the verifiers or not I am keen to hear from folks what other checks should be in it.
abr.kloudle.dev/

2
4
437
During zirp era.
Fastest growing ed tech company of its time.
I get a call early in the morning.
They : Have you changed any AWS settings?
Me : No dude. We don’t do anything outside the scope as per statement of work.
Me : what happened?
They : someone deleted the A record for the internal sales app. Where all the commissions are shown. People are upset.
Me : just checked. That’s a different domain. Not under AWS. This was discussed when we started working with you. This was out of scope.
They : but did you do something.
Me : Nope. Why would we do or work something that’s out of scope and we aren’t getting paid for?
They : …
Me : happy to help you migrate this to the route53 on the access controlled AWS we have configured for you.
So many companies where we highlighted DNS security as a critical laughed at.
Once DNS is compromised even SRI can’t save you.
Defenders get your agent to read the OWASP Third Party JavaScript Management Cheat Sheet.
Once you make sure DNS is secure.

We’re continuing to investigate the security incident. Our DNS server records were compromised through our domain registrar. We are currently unable to receive emails sent to our domain.
Based on our initial investigation this attack targeted the website of a specific customer. We have not seen any indication of a compromise of our internal systems, though we will continue to investigate this.
4
56
10,297