




Pinned Tweet
For anyone using LLMs to do security research, bug bounty, red teaming, etc, we made a Discord to discuss/collaborate: mistakes.io/discord/

I've got a feeling that a lot of security consultants who are being told not to use LLMs on pentests are, in fact, using LLMs on pentests

Since I haven't mentioned this in a while my day still revolves around client conversations like
“We allow frontier models.”
“We don’t allow frontier models.”
“Local inference only.”
“We want you to use Chinese models.”
“We don’t want you to use Chinese models.”
“Frontier models, but only through Bedrock.”
Had some time off of work and was finally able to release a few blog posts: the first is about an RCE on ForgeRock that allowed us (@infosec_au) to remotely send vehicle commands for two automakers using only a customer's name, email, or phone number: samcurry.net/forgerock

The second blog post is about an RCE on a hosting provider that allowed us (@sshell_, @xEHLE_) to steal the WARDOGS server binary, where we could grant unlimited XP and money to any player: samcurry.net/wardogs

It's really cool that you can tick "Paid bug-bounty program running at least 12 months" to prove an organization's security maturity for @AnthropicAI's Red Team Access CVP. As long as they are checking response metrics and stuff, it's probably a better metric than the other two.

We are all in debt to James Kettle

I've been nominated for the SANS Difference Makers Awards, in the Red Teamer category! I'd love your vote: feedback.sans.org/733559
If I win*, I'll share something that genuinely surprised me involving a website, a vulnerability, and GLM 5.3 #SANSDMA #DifferenceMakers
*I'll also share it if I lose
I’d be willing to pay $100 per report for priority triage with automated dupe checking and faster payouts (<48 hours). My experience with this on Immunefi was great, and it’s not a bad way to incentivize researchers to stop abusing teams as the initial assessors of AI reports.


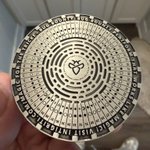
Great challenge coin from @intigriti, so much texture and small details, feels cool to hold


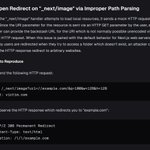
Two years ago, I reported an improper path parsing vulnerability in Next.js. Today, they reported the exact same vulnerability to their competitor, Vinext. Funny coincidence.


We've identified, responsibly disclosed, and confirmed 2 critical, 2 high, 2 medium, 1 low security vulnerabilities in Cloudflare's vibe-coded framework Vinext.
We believe the security of the internet is the highest priority, especially in the age of AI. Vibe coding is a useful tool, especially when used responsibly.
Our security research and framework teams are extending their help and expertise to Cloudflare in the interest of the public internet's security.


Earlier this year, @infosec_au and I discovered multiple vulnerabilities that allowed us to access the back office admin panel of ClubWPT Gold (the World Poker Tour's website) where we could manage customer data, KYC, and more.
Read the writeup here:
samcurry.net/hacking-clubwpt…

Coming back from a bit of a hacking break and have a few blog post drafts written up. Would anyone be interested in reading about hacking online gambling companies, even if the bugs are super simple? So many actuators/easy findings with crazy impact, but nothing very complicated.
Revisiting this before playing the Battlefield 6 beta tonight. Really great blog about hacking a reverse proxy.

Just published a new write-up - Hacking 700 Million Electronic Arts Accounts battleda.sh/blog/ea-account-…

When applying for a job at McDonald's, over 90% of franchises use "Olivia," an AI-powered chatbot. We (@iangcarroll and I) discovered a vulnerability that could allow an attacker to access the over 64 million chat records using the password "123456".
ian.sh/mcdonalds

Huge fan of gadgets like this for pulling info via companies like AWS, Azure, and Cloudflare. Many of these findings aren't serious enough to qualify for bug bounties, but you can 100% use them in the real world for fun recon projects or whatever. Really cool work from @nyxgeek!


