

Real Alerts. Real Pressure. Zero Consequences.
Worldwide
Joined December 2025
- Tweets223
- Following1
- Followers15
- Likes20



Pinned Tweet
KQL is live in the investigations.
Every operation already carried its logs. You could read them. Now you can query them. Nothing to install, no dataset.
What do you run first?
#KQL #SOCSimulator #SOCAnalyst
A clean sandbox verdict is not a clean file. Samples check for accelerated sleeps, small disks, no mouse, lab hostnames. Doing nothing for ninety seconds is a behaviour. How long do you wait?
1

GoAnywhere MFT is live. CVE-2023-0669 on the admin console, a dropped agent, bulk file enumeration, staged exfiltration.
The first honest timestamp you get is a web log line.
1
18
Web and application logs plus the perimeter: socsimulator.com/explore/ope…

5
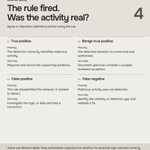
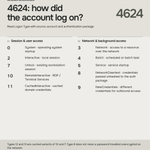
Someone shipped this rule: event 4662 where Properties contains 1131f6aa-9c07-11d1-f79f-00c04fc2dcd2, severity critical.
It has paged the on call every day since.
What is missing from it?
1
6
What a SOC produces is decisions: escalate, contain, ignore. Alerts and tickets are how the decisions get moved around. If your metrics count the packaging, you're measuring the wrong thing.
5

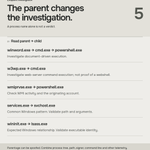
Volt Typhoon: no payload, native binaries in an unusual order, one stolen admin credential, the AD database off the controller, the log wiped.
The room is about spotting the sequence.
1
13
Volt Typhoon: living-off-the-land in critical infrastructure. Advanced, 1h 30m, SIEM, XDR and Firewall. Pro operation.
socsimulator.com/explore/ope…

9
Handover, night to day.
Three pushes denied, the fourth approved two minutes later, all from outside the user's country.
Session is still live. I did not revoke it.
Would you have?
1
9
Revoking ends the access. It also ends your view of what they were reaching for, and they still hold the password: socsimulator.com/explore/ope…

7
Defender exclusions being added, by account:
DeviceProcessEvents
| where ProcessCommandLine has_any
("Add-MpPreference","Set-MpPreference")
| where ProcessCommandLine has_any
("ExclusionPath","DisableRealtimeMonitoring")
The account that ran it is the signal.
1
12

A managed file transfer server is the one box holding every department's files.
Cl0p needed a single request to its admin console to start reading them.
GoAnywhere MFT, CVE-2023-0669, drops Tuesday.
1
1
73
Deserialization on the admin console, then staged exfiltration: socsimulator.com/explore/ope…
1
18
Every rule shipped without an owner, a test and a known false positive rate is a 3am page you haven't received yet. Someone pays for it in attention, and it's usually not the person who shipped it.
1
10
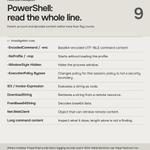
Rule text: process name equals powershell and command line contains -enc.
Three ways past that in under a minute.
Which one does your estate actually see first?
1
16
A completion certificate proves you attended. A stack of alerts you triaged, with the notes you wrote at the time, proves you can think. Employers want the second and keep asking for the first.
10
FrostyGoop is open. The first ICS malware to cause impact through Modbus itself: no exploit, no implant on the controller, just function code 16 writing new setpoints over port 502.
Who watches 502 in your estate?
1
1
18
Pivot from the historian, then read the Modbus stream: socsimulator.com/explore/ope…

1
8
New operations ship every Tuesday at 09:00 UTC, four to six at a time.
Which breach do you wish you could have worked as a live alert queue?
1
12
The schedule runs to 22 December with no empty Tuesdays. Free accounts get ten investigation scenarios in the SIEM console. socsimulator.com/explore/ope…
1
8
The useful line in a handover usually isn't in the template. It's the thing said on the way out the door.
What did you hear last night?
1
9

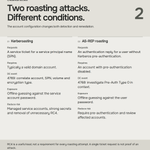
Both tells are Microsoft's own wording: Ticket Encryption Type 0x17 on 4769, and Pre-Auth Type 0 on 4768, which the docs call a security risk. learn.microsoft.com/en-us/pr…

7